Mattermost
mattermost.com
Self-hostable Slack alternative with native desktop, mobile and web apps, and many integrations. There's no end-to-end encryption, so the server can read all messages, and telemetry is on by default. The open source edition caps at 250 users.
- Homepage:mattermost.com
- GitHub:github.com/mattermost/mattermost
- Privacy:mattermost.com/privacy-policy
- iOS App:apps.apple.com/us/app/mattermost/id1257222717
- Android App:play.google.com/.../com.mattermost.rn
- Web info:web-check.xyz/check/mattermost.com
Mattermost Privacy Policy
Privacy Policy Summary
- You are prohibited from sending chain letters, junk mail, spam or any unsolicited messages
- Harming minors in any ways is prohibited
- You are forced into binding arbitration in case of disputes
- You are prohibited from posting content which promotes violence or politically or religiously extremist values
- This service does not guarantee that it or the products obtained through it meet your expectations or requirements
- The service is provided 'as is' and to be used at your sole risk
- Invalidity of any portion of the Terms of Service does not entail invalidity of its remainder
- If you are the target of a copyright claim, your content may be removed
- Failure to enforce any provision of the Terms of Service does not constitute a waiver of such provision
- The service provider makes no warranty regarding uninterrupted, timely, secure or error-free service
- Specific content can be deleted without reason and may be removed without prior notice
- You maintain ownership of your content
- A complaint mechanism is provided for the handling of personal data
- Extra data may be collected about you through promotions
- This service is only available to users over 13 years old
- Defend, indemnify, hold harmless; survives termination
- Instructions are provided on how to submit a copyright claim
- There is a date of the last update of the agreements
- Information is provided about what kind of personal information is collected
- Information is provided about how your personal data is used
- You agree to indemnify and hold the service harmless in case of a claim related to your use of the service
- You must report to the service any unauthorized use of your account or any breach of security
- The service claims to be GDPR compliant for European users
- Third parties used by the service are bound by confidentiality obligations
- Your personal data may be used for marketing purposes
- Your content can be deleted if you violate the terms
- You agree not to use the service for illegal purposes
- Information is provided about how your personal data is collected
- First-party cookies are used
- The service assumes no liability for any damages the user incurs
- Information is gathered about you through third parties
- This service gives your personal data to third parties involved in its operation
- Your account can be deleted or permanently suspended without prior notice and without a reason
- You agree not to submit libelous, harassing or threatening content
- This service tracks which web page referred you to it
- Third-party cookies are used for statistics
- Location data may be collected, used and/or shared
- Your profile is combined across various products
- Your IP address is collected, which can be used to view your approximate location
- Your data may be processed and stored anywhere in the world
- Your personal data is used to employ targeted third-party advertising
- Third-party cookies are employed, but with opt out instructions
- Your personal information is used for many different purposes
- Your personal data is aggregated into statistics
- Your personal data is used for automated decision-making, profiling or AI training
- Your biometric data is collected
- The data retention period is kept to the minimum necessary for fulfilling its purposes
- Your personal data may be sold unless you opt out
- Tracking pixels are used in service-to-user communication
- You can request access, correction and/or deletion of your data
- This service shares your personal data with third parties that are not essential to its operation
- The service claims to be CCPA compliant for California users
- You can opt out of promotional communications
- This service will continue using anonymized user-generated content after erasure of personal information
- You can opt out of targeted advertising
- Many different types of personal data are collected
- You can retrieve an archive of your data
- This service informs you that its Privacy Policy does not apply to third-party services
- The court of law governing the terms is in a jurisdiction that is friendlier to user privacy protection (California, U.S.A.)
- The court of law governing the terms is in the State of California, U.S.A.
- Your personal data may be disclosed to comply with government requests without notice to you
- Your personal data may be sold or otherwise transferred as part of a bankruptcy proceeding or other type of financial transaction
Score
Documents
- Terms of ServiceCreated 06 Apr 21, Last modified 4 months ago
- Privacy PolicyCreated 06 Apr 21, Last modified 4 months ago
- Cookie PolicyCreated 06 Apr 21, Last modified 4 months ago
About the Data
This data is kindly provided by tosdr.org. Read full report at: #2994
Mattermost Source Code
Author

Description
Mattermost is an open source platform for secure collaboration across the entire software development lifecycle..
Homepage
https://mattermost.comRepository
- LicenseOther
- Created15 Jun 15
- Primary languageTypeScript
- Size1,380,390 KB
- Stars39,427
- Forks9,068
- Watchers39,427
Top Contributors
@jwilander (1748)
@hmhealey (1647)
@coreyhulen (1469)
@crspeller (1356)
@agnivade (881)
@it33 (685)
@lieut-data (629)
@hanzei (529)
@enahum (524)
@jespino (393)
@isacikgoz (365)
@saturninoabril (361)
@rgarmsen2295 (342)
@grundleborg (328)
@weblate (318)
@cpanato (254)
@streamer45 (243)
@sbishel (237)
@ConorMacpherson (229)
@mgdelacroix (226)
@pvev (223)
@cursor[bot] (215)
@devinbinnie (209)
@sig1nt (196)
@ccbrown (196)
@wiggin77 (190)
@nickmisasi (187)
@M-ZubairAhmed (181)
@harshilsharma63 (177)
@asaadmahmood (170)
@cpoile (156)
@larkox (154)
@JulienTant (153)
@DavidLu1997 (137)
@marianunez (131)
@jprusch (129)
@jasonblais (124)
@esarafianou (120)
@BenCookie95 (116)
@reflog (110)
@kayazeren (108)
@florianorben (104)
@amyblais (104)
@agarciamontoro (103)
@calebroseland (103)
@rvillablanca (99)
@johnsonbrothers (97)
@Aryakoste (97)
@AGMETEOR (94)
@fsilye (92)
@mkraft (89)
@kaakaa (89)
@mattermod (85)
@unified-ci-app[bot] (79)
@matt-w99 (76)
@DSchalla (70)
@matthewbirtch (66)
@plant99 (58)
@noxer (58)
@mvitale1989 (57)
@mickmister (56)
@lfbrock (53)
@avasconcelos114 (53)
@GoldUniform (52)
@niklabh (52)
@catalintomai (52)
@davidkrauser (51)
@neallred (48)
@metanerd (45)
@koox00 (44)
@ethervoid (44)
@levb (43)
@Syed-Ali-Abbas-Zaidi (39)
@MusikPolice (38)
@Willyfrog (38)
@yasserfaraazkhan (37)
@Gesare5 (36)
@Camillarhi (36)
@toninis (35)
@iomodo (34)
@hahmadia (34)
@RS-labhub (34)
@fmunshi (34)
@vish9812 (33)
@haardikdharma10 (32)
@ashishbhate (30)
@emmyni (30)
@Reinkard (28)
@mattermost-build (28)
@fmartingr (27)
@AshishDhama (27)
@hereje (27)
@gbochora (26)
@csduarte (26)
@carlisgg (24)
@SaurabhSharma-884 (24)
@ZubairImtiaz3 (23)
@enzowritescode (22)
@therealpuneeth20 (22)
@Morgansvk (22)
Recent Commits
[MM-71291] Add a node selector to the System Console server logs (#39320) * [MM-71291] Add a node selector to the System Console server logs On a cluster, the structured log viewer lists the nodes seen in log query responses and can show all nodes or a single node, sending server_names with the query. Rows show their node and search covers it when there are two or more nodes. The time range is also applied client-side for nodes that ignore the server filter, except for the failed-node entry. The choice is saved with the other viewer prefs. * [MM-71291] Keep server-logged node fields and align the log columns Addresses the automated QA findings on the server logs node selector: - Tag each entry with its source node under a symbol key instead of a `node` field. Lines the server logs with its own `node` (cluster join, leave and update) kept losing it from the details, Copy JSON and search. Symbol keys are skipped by JSON.stringify and Object.entries, so Copy JSON and the extra fields need no special casing. - Reserve the scrollbar gutter on the header and the list so the header columns line up with the rows. - Wrap long node names in the Node menu instead of clipping them. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_01AcaavUYo9soMQ1bsfjfHkM --------- Co-authored-by: Claude <[email protected]>
[MM-71341] Report audit logging state from the live audit logger instead of config (#39397) * MM-71341: Report audit logging state from the live audit logger AuditLoggingActive in client config and the ABAC and delivery tracking startup warnings were derived from ExperimentalAuditSettings, so they diverged from what the audit logger was doing after a runtime config edit, a partially applied config, or a target that failed to start. Ask the audit logger's live targets instead. Co-authored-by: mattermost-code <[email protected]> * MM-71341: Test the audit target warnings against the live audit logger Log both warnings through the server logger so tests can observe them, and cover the warnings, the delivery warning's change trigger and the platform's client config default. Co-authored-by: mattermost-code <[email protected]> * MM-71341: Cover the remaining audit target warning conditions Co-authored-by: mattermost-code <[email protected]> * Address PR feedback: 0 answered, 2 resolved, 0 declined --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: mattermost-code <[email protected]>
[MM-71342] Evaluate AUDIT_LOG_OFF offline from the server's recorded audit state (#39395) * [MM-71342] Record the server's audit state in the Support Packet Offline AUDIT_LOG_OFF evaluation re-derived audit activity from the packet's config on the evaluating machine, so the result depended on that machine's environment and platform rather than the server's. The server now records its own IsAuditLoggingActive result in diagnostics.yaml (config.audit_logging_active), and the rule prefers it. Packets from older servers fall back to checking the config. Co-authored-by: mattermost-code <[email protected]> * [MM-71342] Test that a failed diagnostics section falls back to the config Co-authored-by: mattermost-code <[email protected]> * [MM-71342] Use the recorded audit state without requiring the config value Use the real mmctl command fixture in the audit logging packet test. Co-authored-by: mattermost-code <[email protected]> * [MM-71342] Run the audit logging packet test through the registered handler Co-authored-by: mattermost-code <[email protected]> * Address PR feedback: 0 answered, 4 resolved, 0 declined - Rename the recorded value to audit_logging_configured and document that the audit logger applies its targets only at startup. - Add License.HasAdvancedLogging and use it everywhere the advanced logging license check was inlined. - Use the recorded value regardless of config_source collection errors. - Restore the prior audit settings in the support packet test cleanup. --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: mattermost-code <[email protected]>
MM-71344 Plugin API: expose cluster node identity (#39399) * MM-71344 Plugin API: expose cluster node identity Plugins can address cluster events to one node with PluginClusterEventSendOptions.TargetId, but had no way to learn node IDs, their own node's ID, or which node sent an event they received. - Add API.GetClusterNodeID and API.GetClusterNodes, with pluginapi wrappers Cluster.GetNodeID and Cluster.GetNodes. - Add PluginClusterEvent.SourceId, set from a new SourceID prop that both plugin and product publishers attach to outgoing plugin cluster events. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_015bYRkFZXxqdgiFMsh8MPVm * MM-71344 Base plugin cluster identity on cluster membership Enterprise builds register a cluster implementation with an ID even when clustering is disabled, unlicensed or hasn't started, so GetClusterNodeID could return an ID no other node knows. - Add PlatformService.ClusterNodeID, which returns the ID only once the node has joined (GetMyClusterInfo is non-nil). GetClusterNodeID and GetClusterNodes both use it, so they agree. - GetClusterNodes leaves out registered-but-disconnected nodes, whose Id is a registration ID that can't be used as a TargetId. - Drop the SourceID prop from the product publisher: nothing calls it and the receiver drops its messages for lack of a PluginID. - Document that SourceId is empty for events from older nodes. - Tests: cover the not-joined case and disconnected nodes, share one test helper across cluster cases, drop redundant setup. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_015bYRkFZXxqdgiFMsh8MPVm * MM-71344 Target 12.2 as the minimum server version Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_015bYRkFZXxqdgiFMsh8MPVm * MM-71344 Drop SourceId note from OnPluginClusterEvent doc Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_015bYRkFZXxqdgiFMsh8MPVm --------- Co-authored-by: Claude <[email protected]>
[MM-71218] Count env var audit targets in IsAuditLoggingActive (#39243) * [MM-71218] Count env var audit targets in IsAuditLoggingActive configureAudit merges audit targets from MM_EXPERIMENTALAUDITSETTINGS_ADDITIONAL, regardless of license, but IsAuditLoggingActive and IsAuditLevelActive only looked at ExperimentalAuditSettings. A server auditing through the env var then logged a false "no active audit log target" warning at startup and reported AuditLoggingActive=false in the client config. Share the env var parsing through config.AdditionalAuditConfig and merge those targets before checking audit levels. Co-authored-by: mattermost-code <[email protected]> * [MM-71218] Treat malformed additional audit config as inactive configureAudit returns before Configure when MM_EXPERIMENTALAUDITSETTINGS_ADDITIONAL is unparseable, so licensed advanced targets are never applied. Report IsAuditLoggingActive/IsAuditLevelActive as inactive in that case. Co-authored-by: mattermost-code <[email protected]> * Address PR feedback: 1 answered, 7 resolved, 0 declined Share EffectiveAuditConfig between configureAudit and the audit activity checks so the checks match what the server applies: the basic _defAudit target is merged and overridable, invalid env var targets report inactive, and the env var is read once. Rename hasAdvancedAuditTarget to hasAuditTargetFor and mention MM_EXPERIMENTALAUDITSETTINGS_ADDITIONAL in the ABAC and delivery warnings. * Address PR feedback: 0 answered, 2 resolved, 0 declined * [MM-71218] Give audit rule test a file name for enabled file audit Co-authored-by: mattermost-code <[email protected]> * [MM-71218] Validate syslog TLS cert when checking audit activity Co-authored-by: mattermost-code <[email protected]> * Address PR feedback: 0 answered, 3 resolved, 1 declined * Address PR feedback: 0 answered, 1 resolved, 0 declined --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: mattermost-code <[email protected]>
[MM-70757] Docs: Site health dashboard (#39255) * docs: AI draft for #39064 * docs: drop API endpoints and 403 detail from Site health page * docs: expand Site health page with checks, severities, cadence, and license * docs: state Site health plan availability plainly * docs: add Site health to sidebar, cover mmctl and related pages * docs: simplify muted-by description * docs: Site health dashboard requires v12.2 * docs: address review on Site health categories and mmctl --packet * docs: drop version-support note from mmctl packet section * docs: clarify unmute destination and mmctl --packet restriction --------- Co-authored-by: mattermost-docs-ai[bot] <41898282+github-actions[bot]@users.noreply.github.com>
MM-67333: Update remote cluster response handling (#38710) * MM-67333: Update remote cluster response handling Introduce a shared maximum response size in the remotecluster package and route the three outbound peer reads through it, so the reply a peer returns is read the same way at every call site. Co-authored-by: mattermost-code <[email protected]> * MM-67333: Prefer HTTP status when a remote reply is too long to read When a remote replies with a non-OK status, report that status even if the body is longer than we read. Co-authored-by: mattermost-code <[email protected]> * Address PR feedback: 0 answered, 7 resolved, 0 declined * Address PR feedback: 0 answered, 3 resolved, 0 declined --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: mattermost-code <[email protected]>
Migrate channel action tiles to Compass TileButton (#39030) * Migrate action buttons to Compass ActionButton component - top_buttons.tsx: Replace custom styled Button/CopyButton with ActionButton. Drop flex:1 stretch in favour of flex+gap layout with fixed 88px tiles. Drop green 'Copied' success flash; use label/icon swap only. Migrate icons to compass-icons components wrapped in Icon. - channel_intro_message.tsx: createFavoriteButton → ActionButton; createSetHeaderButton / createNotificationPreferencesButton replaced by SetHeaderButton / NotificationPrefsButton functional sub-components that dispatch openModal directly (no ToggleModalButton wrapper). - add_members_button.tsx: MoreThanMaxFreeUsers tile migrated from ToggleModalButton+action-button to ActionButton with direct dispatch. - pluggable_intro_buttons.tsx: Replace button.action-button with ActionButton. - _action-button.scss: Retire global stylesheet; no remaining usages. - channel_intro_message.test.tsx: Drop stale toHaveClass('action-button') assertions that no longer apply to the Compass component. Co-authored-by: Matthew Birtch <[email protected]> * Fix ESLint failures in Compass ActionButton channel intro migration Reorder imports, move useCallback above the archived-channel early return, and split NotificationPrefsButton props across lines to satisfy lint rules. Co-authored-by: Matthew Birtch <[email protected]> * Fix openModal typing for channel intro add-members button Split group-constrained vs invite openModal calls so dialogType and dialogProps are not a union that fails tsc under ModalData. Co-authored-by: Matthew Birtch <[email protected]> * Use Compass Icon slots without glyph size overrides Co-authored-by: Matthew Birtch <[email protected]> * Use spacing-xs gap for channel intro actions Co-authored-by: Matthew Birtch <[email protected]> * Fit RHS ActionButtons in one row with spacing-xs gap Co-authored-by: Matthew Birtch <[email protected]> * Localize channel intro favorite button aria-label Convert createFavoriteButton into a FavoriteButton component that uses formatMessage for Favorited/Favorite, matching SetHeaderButton and RHS top buttons so screen readers get a localized state-aware label. Co-authored-by: Matthew Birtch <[email protected]> * Fix ActionButton a11y: toggles use active, dialogs use aria-haspopup Compass ActionButton.active maps to aria-pressed (toggle pattern). Stop passing active for Add People (dialog opener) and use aria-haspopup / aria-expanded instead. Apply the same dialog semantics on intro modal triggers. Co-authored-by: Matthew Birtch <[email protected]> * Drop aria-expanded from the Add People dialog trigger aria-haspopup=dialog already marks the button as a dialog opener. aria-expanded is for menus and disclosures, so remove it and the isInvitingPeople state that only fed that attribute. Co-authored-by: Matthew Birtch <[email protected]> * Pass channel dialogProps to AddGroupsToChannelModal Restores the prop ToggleModalButton always supplied on master so the modal keeps the selected channel if the user navigates before submit. Co-authored-by: Matthew Birtch <[email protected]> * Make AddGroupsToChannelModal extra own props optional The modal already treats skipCommit, onAddCallback, and excludeGroups as optional. The connector required them, so passing dialogProps: {channel} failed check-types. Co-authored-by: Matthew Birtch <[email protected]> * fix a11y issue with toggle favorite/mute * Bump @mattermost/compass-ui to 0.1.0-alpha.20 Picks up ActionButton label wrapping (two lines, then ellipsis) so long translated labels no longer overflow the button. Co-Authored-By: Claude <[email protected]> * Update snapshots for compass-ui alpha.20 Radio class hashes The compass-ui bump regenerated CSS-module class name hashes for Radio. Snapshot diffs are hash-only; no markup changes. Co-Authored-By: Claude <[email protected]> * Add tests for channel intro ActionButton migration Cover aria-pressed on Favorite, aria-haspopup and modal dispatch on Set header, Notifications and Add people (including the group_constrained branch), and the plugin intro buttons. Co-Authored-By: Claude <[email protected]> * Bump @mattermost/compass-ui to 0.1.0-alpha.21 and migrate to TileButton ActionButton was renamed to TileButton and its `active` prop to `toggled` in alpha.21. Update the channel info RHS and channel intro usages. Co-Authored-By: Claude <[email protected]> * Update snapshots for compass-ui alpha.21 Button class hashes compass-ui alpha.21 changed the Button CSS class hashes (for example _button_aa8j5_2 is now _button_we8pe_2), so three snapshots were out of date. Most of the change is those hashes. One small markup change also shows up: the Button icon slot span no longer has aria-hidden="true". The icon inside it still has its own aria-hidden="true". This affects the send test notification notice and the notification settings snapshots. Co-Authored-By: Claude Sonnet 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_01WiZSFstuJUYC3WewycGGfu --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: Matthew Birtch <[email protected]> Co-authored-by: Claude <[email protected]> Co-authored-by: mattermost-code <[email protected]>
mmctl: migrate system command context.TODO() to cmd.Context() (#37371) * mmctl: migrate system command context.TODO() to cmd.Context() Scoped subset of #36995: threads cobra command context through the mmctl system subcommands (getbusy/setbusy/clearbusy/version/status/ supportpacket/nuke users) via a new cmdContext() helper, and wires Ctrl+C/SIGTERM cancellation into RootCmd via signal.NotifyContext so in-flight API calls are cancelled cleanly on interrupt. Co-Authored-By: Claude Sonnet 5 <[email protected]> Claude-Session: https://claude.ai/code/session_01J3cohMg7NnYcRhmggs2fjP * mmctl: drop nil-safe cmdContext(), call cmd.Context() directly cobra guarantees a non-nil cmd.Context() once RootCmd.ExecuteContext() runs, so the nil-fallback wrapper only existed to paper over unit/e2e tests that call command handlers directly on a bare &cobra.Command{}. Push that concern into the tests instead: add a newTestCmd(t) helper that binds a context to the test's lifetime, and use it everywhere tests construct a cobra.Command for a system-command handler. * mmctl: reuse real command vars in tests instead of re-declaring flags system_test.go and system_e2e_test.go each redeclared the output-file, confirm, and seconds flags on a bare cobra.Command, duplicating the registration already done in system.go's init(). Extend newTestCmd to optionally bind context onto one of those real command vars, and set only the value under test via Flags().Set() instead of re-registering the flag. * mmctl: extract shared SystemPingOptions literal in system_test.go The gomock.Any(), model.SystemPingOptions{FullStatus: true, RESTSemantics: true} expectation was repeated identically across all eight TestServerStatusCmd subtests. Extract it into a single systemPingOpts var. * mmctl: scope systemPingOpts to TestServerStatusCmd It was only used by this test's eight subtests, so a package-level var was wider scope than needed. * mmctl: fix Ctrl+C hang, test state leakage, and helper footguns from review - root.go: restore default signal handling as soon as the context is canceled (on the first Ctrl+C/SIGTERM), not only after ExecuteContext returns, so a second signal still kills the process if a command is blocked on something that doesn't observe context cancellation (e.g. auth.go's interactive login prompt, or the Windows nuke-users confirmation prompt). Also broaden the suppressed-error check to context.DeadlineExceeded and extract the flush/print logic into a finishExecute helper shared with root_test.go's executeRoot, so the tests exercise the same code Run() runs instead of a hand-copied duplicate. - mmctl_test.go: newTestCmd takes a single *cobra.Command (nil for a flagless command) instead of a variadic, and its cleanup resets the reused command's context and every flag back to its default. This fixes flag/context leakage across tests that reuse the same package-level command var (e.g. SystemNukeUsersCmd's "confirm", SystemSetBusyCmd's "seconds"), removes the now-redundant manual output-file reset in system_test.go/system_e2e_test.go, and avoids an unconditional throwaway allocation when a base command is passed. * mmctl: fix staticcheck SA1012 and tidy go.mod for pflag Passing a literal nil context.Context trips staticcheck's SA1012 even though it's the correct way to restore cobra's own "no context assigned yet" sentinel; suppress it with the codebase's established //nolint:staticcheck convention and explain why. Also run `make modules-tidy` to promote github.com/spf13/pflag from an indirect to a direct dependency now that mmctl_test.go imports it directly. * mmctl: add CLAUDE.md capturing test conventions from review Codifies the test-state-leakage, flag-reuse, and fixture-scoping fixes made in this branch so future changes follow the same pattern. Co-Authored-By: Claude Sonnet 5 <[email protected]> * mmctl: require newTestCmd callers to pass a real command var nil silently type-checks for any command's test, so a copy-pasted subtest that should bind a flagged command (e.g. SystemSetBusyCmd) can keep compiling against nil and quietly skip flag reset. Drop the nil shortcut and update callers to pass the matching command var. Co-Authored-By: Claude Sonnet 5 <[email protected]> * mmctl: point CLAUDE.md test note at newTestCmd directly The prior wording spelled out newTestCmd's cleanup mechanism instead of just naming the helper to use. Co-Authored-By: Claude Sonnet 5 <[email protected]> * mmctl: dedupe printer.Clean() in system tests via Run helpers RunForSystemAdminAndLocal/RunForAllClients now call printer.Clean() once per client subtest, so callers no longer repeat it as the first line of every closure. Applied to the three system_e2e_test.go call sites that use these helpers. Also drops TestSetBusyCmd/SetBusy_with_missing_arg: it only passed because the old bare-cobra.Command test double had no "seconds" flag registered, so cmd.Flags().GetUint errored. setBusyCmdF ignores args entirely, so the subtest never exercised missing-arg validation, and with the real SystemSetBusyCmd (a registered flag with a valid default) that error path is unreachable through real CLI dispatch. Co-Authored-By: Claude Sonnet 5 <[email protected]> * mmctl: note that Run helpers already reset the printer Co-Authored-By: Claude Sonnet 5 <[email protected]> * mmctl: address review feedback on signal handling and test cleanup - Use context.AfterFunc to restore default signal handling. - Stop suppressing context.DeadlineExceeded: net and http transport timeouts match it, so mmctl exited 1 without printing the error. - Clean the printer in MmctlE2ETestSuite.SetupSubTest instead of in each RunFor* helper. Co-Authored-By: Claude Opus 5.5 <[email protected]> * mmctl: use go.uber.org/mock in system tests --------- Co-authored-by: Claude <[email protected]> Co-authored-by: Mattermost Build <[email protected]>
MM-68613: resize message columns only on fresh installations (#39332)
Monthly maintenance (2026-10): Upgrade golangci-lint (#39221) * Upgrade golangci-lint to v2.15.0. Disable exhaustruct_v5, which replaces the already disabled exhaustruct linter, and apply the new modernize simplifications. Co-authored-by: jesse <[email protected]> * Retrigger CI after E2E dispatch-run job-name collision. Co-authored-by: mattermost-code <[email protected]> * Address PR feedback: 1 answered, 3 resolved, 0 declined --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: jesse <[email protected]> Co-authored-by: mattermost-code <[email protected]>
Add registerChannelViewComponent so plugins can replace the channel center view (#39281) * Add registerChannelViewComponent plugin registry method for replacing the channel center view Adds a generic webapp plugin API that lets a plugin render its own component in place of a channel's post list and message composer, for channels selected by a plugin-supplied matcher. The channel header, channel banner, and bookmarks bar remain rendered by core. API: registry.registerChannelViewComponent({matcher, component, handlesPermalinks}): string (positional form registerChannelViewComponent(matcher, component, handlesPermalinks) also works) - matcher: (state: GlobalState, channel: Channel) => boolean Receives the full Redux state; only an exact `true` counts as a match. Throws are caught, logged once per plugin, and treated as no-match. First match wins, in reducer order (alphabetical pluginId, then insertion order). - component: React.ComponentType<ChannelViewPluginComponentProps> Props: {channel: Channel; channelId: string; teamId: string; focusedPostId?: string}, where teamId is the current team's id. Rendered inside <div id="channelViewPluginComponent"> and a PluggableErrorBoundary. - handlesPermalinks?: boolean (default false) When a channel is opened via a permalink (/:team/channels/:name/:postid), core renders its normal post list and composer so the linked post is still shown and highlighted, unless the registration sets handlesPermalinks: true, in which case the plugin component is rendered and receives the linked post id as focusedPostId. The core view persists for that visit after the post id is dropped from the URL, until the user switches channels. - Returns an id usable with unregisterComponent; registrations are removed automatically when the plugin is removed. When a registration is rendered, ChannelView does not render the post list, the composer, or the archived/deactivated/restricted-DM notices that replace the composer. Because PostList (which normally marks the channel as read after loading posts) is not mounted, the plugin view wrapper dispatches markChannelAsRead on mount and whenever the channel changes. Marking on window focus and on new posts is already handled globally (team_controller's markAsReadOnFocus, actions/new_post) and applies unchanged. Matching is resolved by the new getChannelViewPluginComponent selector (selectors/channel_view_plugin.ts), wired through channel_view's mapStateToProps. Co-authored-by: Joram Wilander <[email protected]> * Require channel view plugins to handle permalinks. A registration always replaces the center view, including when the channel is opened on a post. The plugin receives that post id as focusedPostId. Co-authored-by: Cursor <[email protected]> * Address channel view review comments. Skip marking a plugin channel read on a permalink, clear the channel-switch perf marks the post list would have cleared, and keep the header mounted when the center swaps to the plugin view. Co-authored-by: Cursor <[email protected]> * Share the channel-switch performance mark cleanup. The post list and a plugin channel view both have to clear the same click marks, so a change to that set stays in one place. Co-authored-by: Cursor <[email protected]> * Fix import order in the plugin channel view. Co-authored-by: Cursor <[email protected]> * Retrigger CI. Co-authored-by: Cursor <[email protected]> --------- Co-authored-by: Cursor Agent <[email protected]>
docs: document bot attributes (#39224) * docs: document bot attributes and clarify ABAC policies apply to bots Co-authored-by: Cursor <[email protected]> * docs: remove EnableUserManagedAttributes note for bot owners Remove the note about bot owners setting Member values when EnableUserManagedAttributes is enabled, as this was for testing purposes only and doesn't need to be documented. Co-authored-by: Maria A Nunez <[email protected]> --------- Co-authored-by: Cursor <[email protected]>
Migrate DoubleCheckPassword from *model.AppError to error. (#39379) The function returns nil, an AppError it builds itself, or checkUserPassword's error after a nil check, so the model.AsAppError adapter from the password-check drip is no longer needed. Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: jesse <[email protected]>
[MM-71290] Apply log filters on all cluster nodes (#39319) * [MM-71290] Apply log filters on all cluster nodes Pass the logs query filter through ClusterInterface.QueryLogs so remote nodes filter by level and date themselves, and document that a node whose logs can't be fetched is reported as a single error entry instead of failing the request. * Trim QueryLogs API docs Drop the paragraph restating that filters apply on every node (already covered by the release note) and note that nodes the cluster has marked as failed are omitted from the response. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_01AYnv2eNo1pjDXsHdZgwwQ6 * Return per-node errors from ClusterInterface.QueryLogs QueryLogs now returns an einterfaces.NodeLogs per node, with Err set when a node's logs couldn't be fetched. Server.QueryLogs turns that error into the synthetic error log entry, so the API response is unchanged while the cluster layer no longer formats log lines. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_01AYnv2eNo1pjDXsHdZgwwQ6 --------- Co-authored-by: Claude <[email protected]>
[MM-71289] Fix server_names filter in logs query (#39318) Return local logs when server_names names this node by its cluster hostname (or "default"), skip the cluster round-trip when only the local node is requested, and stop emitting null entries for names that don't match a node. Remote nodes are only queried on a licensed, enabled cluster, matching how the local node name is chosen.
fix(e2e): restore CollapsedThreads in the per-test config reset (#39377)
The rules a new translation is held to (#39299) * Report a catalog that cannot be read or is not an object, rather than crash A locale catalog whose top level was null, a number or a string made check_icu.mjs throw, and an array was checked as if it were an empty catalog; a catalog it could not read threw too. Either way the run ended at that file, so the catalogs after it went unchecked. Each is now an error against its file, and the rest are checked. en.json is held to the same shape: an array or a number left nothing to check, and every catalog passed. mmgotool i18n verify already reports each of these and carries on. Co-authored-by: Jesse Hallam <[email protected]> * Keep a copy of go-i18n's server plural forms, pinned by a Go test The translation rules check a server plural map in Node, before the catalog is written, so they need go-i18n's plural categories for each locale. i18n/scripts/lib/server_plurals.json holds them, and a Go test fails if it disagrees with go-i18n for any server catalog, or lists a locale with none. The server translation job runs the test, so a PR that adds a server locale has to add it to the table. Co-authored-by: Jesse Hallam <[email protected]> * Hold a new translation to the structural rules, and test them in CI i18n/scripts/lib/rules.mjs checks one translation, before it is written to a catalog. Webapp messages go through icu_rules.mjs, the code check_icu.mjs runs, so the two cannot disagree; what CI tolerates as a warning in the catalogs as they stand is an error for new work, except an arrow in a right-to-left locale, which is soft. Server messages get the per-string checks mmgotool i18n verify makes, with plural forms held to go-i18n's table rather than CLDR. icu_rules.mjs gains plural-unused-category, a plural arm the locale never selects. check_icu.mjs does not report it: it is dead text, not something a user sees, so it is left to the pipeline. A new job runs the pipeline's tests, and the workflow now runs for a change under i18n/. Co-authored-by: Jesse Hallam <[email protected]> * Flag a translation that leaves out a name the glossary keeps in English A doNotTranslate term (Mattermost, GitLab, Markdown) dropped from a translation is a soft finding: usually a mistake, sometimes a sentence that is better leaving the brand implicit, so it lands only with a stated reason. Channels, Playbooks, Boards and Calls are product names that are also ordinary English words. The English reads the same whether a string names the product or starts a sentence about channels, so they are marked commonWord and not flagged; the translator decides from the description. Co-authored-by: Jesse Hallam <[email protected]> * Catch English left untranslated A translation identical to its English is an error once the English has three ordinary lowercase words, a sentence nobody translated, and soft below that, where it may be a name or a word the language shares with English. In a language not written in Latin script, lowercase English words kept from the source are soft too. Only words a translator would translate count: ICU arguments and tags, template actions, URLs, email addresses, glossary names, quoted values and anything shaped like an identifier are left out. en-* locales are not checked. icu_rules.mjs exports its parser and options, so the rules read a message's literal text the way check_icu.mjs parses it. Co-authored-by: Jesse Hallam <[email protected]> * Flag the wrong form of address i18n/style.json records, for each locale where the choice matters, how its catalogs address the user, formally or informally, and the pronouns that would mean the other. A translation that uses one is soft: a pronoun can be quoted text or mean someone else, as German "Sie" can at the start of a sentence, so a stated reason lets it land. Co-authored-by: Jesse Hallam <[email protected]> * Check the glossary and style files in CI The translation rules read i18n/glossary/ and i18n/style.json, so a malformed entry would quietly change what a translation is held to. check_glossary.mjs holds them to their shape: canonical JSON, the known fields only, one owner per term or alias, a glossary file for exactly the locales with catalogs, terms in en.json order, a doNotTranslate term's target the term itself, and no pronoun both used and avoided. Co-authored-by: Jesse Hallam <[email protected]> * Run every translation check through make i18n-verify-all CI ran the i18n checks as three jobs of inline commands: the webapp checker, make i18n-verify plus the plural-table test in the build container, and the pipeline's tests and glossary check. Nobody could run that set locally without copying it out of the workflow. make i18n-verify-all in server/ now runs all of them, and CI runs only that, in one job on the runner. Go comes from setup-go at mmgotool's go.mod version, as Tools CI does, so the build container, and with it the Docker Hub secrets and id-token permission it needed, are gone. The workflow also runs when server/Makefile changes. Co-authored-by: Jesse Hallam <[email protected]> * Run make i18n-verify-all in the build environment again The previous commit swapped the build environment for setup-go, for no reason that holds up: the image has the Node .nvmrc pins as well as the Go mmgotool needs, it reuses the Go caches Server CI warms, and it mounts the checkout, so it sees the node_modules webapp-setup installs. Server CI builds and checks in it too. Co-authored-by: Jesse Hallam <[email protected]> * Drop comments that only restate the code Each said what the line under it already says: a path list, a setup step, a target its help text describes, a function its name and body describe, and how to run tests the Makefile now runs. Comments that give a reason the code cannot show stay. Co-authored-by: Jesse Hallam <[email protected]> * Fail on a glossary or style file that is not a JSON object readGlossary and readStyle read an array or a number as an empty glossary or no style, which turned the do-not-translate and form-of- address rules off without a word, and threw an unrelated TypeError on null. check_glossary.mjs rejects these shapes in CI, but the rules read the files on their own. Each is now an error naming the file; a file that does not exist still means none. Co-authored-by: Jesse Hallam <[email protected]> --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: Jesse Hallam <[email protected]>
[MM-70939] Improve tests for plugin identity and cancellation (#38822) * [MM-70939] Cover plugin dispatch identity and cancellation * [MM-70939] Account for stream deadline race in dispatch tests
Add hideRoot to the thread viewer and publish the file preview modal (#39280) * Add getThreadViewer to the plugin registry. Co-authored-by: Joram Wilander <[email protected]> Co-authored-by: Cursor <[email protected]> * Add hideRoot so the thread viewer can list replies without repeating the root post. Co-authored-by: Cursor <[email protected]> * Publish the file preview modal so plugins can open core's previewer. Co-authored-by: Cursor <[email protected]> * Keep the new-messages line when hideRoot omits the root post. The separator selector skips the oldest post, which is the root. Removing the root before that step made the first unread reply look already seen. Co-authored-by: Cursor <[email protected]> * Fix import order in thread viewer test. Co-authored-by: mattermost-code <[email protected]> * Fix type errors in thread viewer test. Co-authored-by: mattermost-code <[email protected]> * Remove getThreadViewer from the plugin registry. window.Components.ThreadViewer already exports the same component. Co-authored-by: Cursor <[email protected]> * Test withoutRoot date-line handling directly. Co-authored-by: Cursor <[email protected]> * Hide a join/leave root before its id is combined. Co-authored-by: Cursor <[email protected]> --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: mattermost-code <[email protected]>
Fix flaky TestGetUserStatus/dnd_status_timed_restore_after_time_interval (#39354) Automatic Merge
Reject Redis cache prefixes that could match another server's keys (#39329)
Migrate checkboxes to Compass Checkbox (full stack) (#39040) * Migrate checkbox setting adapters to Compass Checkbox Replace native checkbox inputs in CheckboxSetting, CheckboxSettingItem, and CheckboxGroupSetting with @mattermost/compass-ui/components/checkbox. Add flex-reverse styling for apps form label_position before. Update related Jest tests and snapshot. Co-authored-by: Matthew Birtch <[email protected]> * Fix import/order for Compass Checkbox adapter imports. Co-authored-by: Cursor <[email protected]> * Update CheckboxSetting snapshot for current Compass CSS module hashes. Co-authored-by: Cursor <[email protected]> * Add CheckboxSettingItem tests for Compass Checkbox migration. Co-authored-by: Cursor <[email protected]> * Migrate Classification Markings clearance checkbox to Compass Checkbox Replace the native clearance attribute checkbox with @mattermost/compass-ui Checkbox, keeping data-testid, checked/disabled/onChange, and FormattedMessage label children. Update the clearance notice test to assert the accessible name. Co-authored-by: Matthew Birtch <[email protected]> * Migrate Push Settings HPNS ToS checkbox to Compass Checkbox Replace the native HPNS Terms of Service acceptance input with @mattermost/compass-ui Checkbox while preserving FormattedMessage links and form-group layout. Co-authored-by: Matthew Birtch <[email protected]> * Update Push Settings snapshot for Compass Checkbox Refresh the licensed HPNS ToS checkbox snapshot after migrating to @mattermost/compass-ui Checkbox. Co-authored-by: Matthew Birtch <[email protected]> * Fix import/order for Compass Checkbox in Push Settings. Co-authored-by: Cursor <[email protected]> * Migrate ChannelsResourceSettings location checkboxes to Compass Checkbox Replace custom Header/Banner checkbox markup with @mattermost/compass-ui Checkbox. Leave the Required role=switch control unchanged. Co-authored-by: Matthew Birtch <[email protected]> * Fix import/order for Compass Checkbox in ChannelsResourceSettings. Co-authored-by: Cursor <[email protected]> * Migrate FilterCheckbox to Compass Checkbox Replace the native dual-input FilterCheckbox pattern with a controlled @mattermost/compass-ui Checkbox, wire toggles through onChange only, and drop FilterList_checkbox input styles that conflict with Compass. Co-authored-by: Matthew Birtch <[email protected]> * Migrate Commercial Support Modal packet checkboxes to Compass Checkbox Replace native input+label pairs for Support Packet contents with @mattermost/compass-ui Checkbox and drop obsolete label SCSS. Co-authored-by: Matthew Birtch <[email protected]> * Space FilterList checkbox items with --spacing-xs gap Wrap filter option items in FilterList_items and use a flex column gap of var(--spacing-xs) (8px) so Management checkboxes are not stacked flush. Co-authored-by: Matthew Birtch <[email protected]> * Update CommercialSupportModal snapshot for Compass Checkbox Co-authored-by: Matthew Birtch <[email protected]> * Fix import/order lint for Compass Checkbox imports Co-authored-by: Cursor <[email protected]> * Migrate Access Control channel list auto-add checkboxes to Compass Checkbox Replace native header and per-row auto-add inputs with @mattermost/compass-ui Checkbox, using the indeterminate prop for mixed bulk state, and keep stable ids/data-testids for Playwright selectors. Co-authored-by: Matthew Birtch <[email protected]> * Fix ChannelList auto-add checkbox label spacing Compass Checkbox defaults to width 100%, which stretched the control across the DataGrid header cell and separated the sibling label. Put header and row labels as Checkbox children and constrain width so the control stays compact next to the info tooltip. Co-authored-by: Matthew Birtch <[email protected]> * Polish ChannelList auto-add checkbox layout and typography Remove redundant left padding, use semi-bold header label, left-align the column, and use flex instead of inline-flex so On/Off no longer shifts row height. Co-authored-by: Cursor <[email protected]> * Fix stylelint property order and eol-last in ChannelList checkbox migration. Co-authored-by: Cursor <[email protected]> * Migrate LDAP Groups list checkboxes to Compass Checkbox Replace custom group-check and filter-check controls in GroupRow and GroupsList with @mattermost/compass-ui Checkbox. Selection is owned by the checkbox (no full-row click toggle) so link/unlink actions are not double-toggled. Update related SCSS and Jest tests. Co-authored-by: Matthew Birtch <[email protected]> * Update GroupRow and GroupsList snapshots for Compass Checkbox Co-authored-by: Matthew Birtch <[email protected]> * Migrate Channel Moderation Guests/Members checkboxes to Compass Checkbox Replace custom button checkboxes in ChannelModerationTableRow with @mattermost/compass-ui Checkbox, preserving data-testid wiring and disabled/checked behavior for scheme-disabled permissions. Co-authored-by: Matthew Birtch <[email protected]> * Update Channel Moderation snapshots for Compass Checkbox Co-authored-by: Matthew Birtch <[email protected]> * Fix import/order for Compass Checkbox in LDAP Groups list. Co-authored-by: Cursor <[email protected]> * Fix import/order for Compass Checkbox in Channel Moderation. Co-authored-by: Cursor <[email protected]> * Migrate settings modal checkboxes to Compass Checkbox Replace remaining native checkbox inputs in Account Settings, channel/team settings modals, and CheckboxWithSelectSettingItem with @mattermost/compass-ui Checkbox while preserving behavior. Co-authored-by: Matthew Birtch <[email protected]> * Update settings modal checkbox snapshots for Compass Checkbox Co-authored-by: Matthew Birtch <[email protected]> * Fix Bootstrap left padding on settings-modal Compass Checkboxes Mirror #39130: Bootstrap .checkbox label { padding-left: 20px } was for native inputs with margin-left: -20px. Compass Checkbox is itself a label, so add the existing .no-padding escape hatch on Account Settings wrappers and zero label padding under .checkbox.single-checkbox in settings SCSS. Co-authored-by: Matthew Birtch <[email protected]> * Restore Theme apply-to-all-teams space before Save/Cancel .checkbox.no-padding sets padding: 0 and was overriding .user-settings__submit-checkbox padding-bottom. Move that gap to margin-bottom so Compass left-padding fix and vertical spacing coexist. Co-authored-by: Matthew Birtch <[email protected]> * Beat Bootstrap form-horizontal zeroing Theme checkbox margin .form-horizontal .checkbox sets margin-bottom: 0 at higher specificity than .user-settings__submit-checkbox, so the spacing restore never applied. Raise the selector to .form-horizontal .checkbox.user-settings__submit-checkbox. Co-authored-by: Matthew Birtch <[email protected]> * Fix import/order for Compass Checkbox imports Co-authored-by: Cursor <[email protected]> * Lay out channel display location checkboxes side-by-side with 24px gap. Co-authored-by: Cursor <[email protected]> * Space Commercial Support Modal packet checkboxes with a gap container. Co-authored-by: Cursor <[email protected]> * Use translated titles in Channel Moderation checkbox aria-labels. Co-authored-by: Cursor <[email protected]> * Migrate Integrations backstage checkboxes to Compass Checkbox Replace native checkbox inputs on incoming webhooks, slash commands, and bot forms with @mattermost/compass-ui Checkbox and align them via a backstage-form helper class. Co-authored-by: Cursor <[email protected]> * Fix Cypress selectors after Compass Checkbox migration. Wire allowedDomainsCheckbox data-testid onto the Compass input and update team settings E2E specs that still queried the removed native checkbox class. Co-authored-by: Matthew Birtch <[email protected]> * Update PushSettings snapshot for Compass Checkbox CSS module hashes. Co-authored-by: Matthew Birtch <[email protected]> * Update admin console snapshots for FilterCheckbox Compass migration. Co-authored-by: Matthew Birtch <[email protected]> * Fix channel_moderation operator-linebreak lint after Compass Checkbox migration. Co-authored-by: Matthew Birtch <[email protected]> * Update ChannelList auto-add snapshots for Compass Checkbox migration. Co-authored-by: Matthew Birtch <[email protected]> * Update LDAP Groups snapshots for Compass Checkbox migration. Co-authored-by: Matthew Birtch <[email protected]> * Update channel settings access rules snapshot for Compass Checkbox. Co-authored-by: Matthew Birtch <[email protected]> * Fix TeamAccessTab test for allowedDomainsCheckbox data-testid. Allowed domains is not gated on INVITE_USER; the previous assertion only passed because the test id never reached the DOM before the Compass migration. Co-authored-by: Matthew Birtch <[email protected]> * Update PolicyDetails snapshots for ChannelList Compass Checkbox migration. Co-authored-by: Matthew Birtch <[email protected]> * Update notification settings snapshots for Compass Checkbox migration. Co-authored-by: Matthew Birtch <[email protected]> * Update checkbox_group E2E to assert Compass label-before flex layout. Compass Checkbox keeps input-then-label DOM order; label_position before is implemented with flex-direction row-reverse rather than reordering nodes. Co-authored-by: Matthew Birtch <[email protected]> * Update channel moderation E2E for Compass Checkbox opacity and checked state. Native inputs are opacity:0; interact with force and assert the checked property instead of Bootstrap checkbox CSS classes. Co-authored-by: Matthew Birtch <[email protected]> * Update timezone display E2E for Compass Checkbox opacity-0 input. Co-authored-by: Matthew Birtch <[email protected]> * Force-uncheck automatic timezone checkbox in invalid-input E2E path. Co-authored-by: Matthew Birtch <[email protected]> * Support Bootstrap and Compass checkboxes in channel moderation E2E helpers. System/team scheme permission widgets still use Bootstrap checked classes; channel moderation uses Compass native inputs. Detect both so scheme toggles work again after the Compass migration. Co-authored-by: Matthew Birtch <[email protected]> --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: Matthew Birtch <[email protected]> Co-authored-by: mattermost-code <[email protected]>
Add dot release docs for server v12.0.1, v11.11.3, v11.10.4, v11.7.14 (ESR) and v10.11.25 (ESR) (#39357) * Add dot release docs for v12.0.1, v11.11.3, v11.10.4, v11.7.14 and v10.11.25 Document the October 22, 2026 patch releases from the release-branch notes, and point download, SBOM, and archive links at those versions. Co-authored-by: Amy Blais <[email protected]> * Update mattermost-v11-changelog.mdx * Update mattermost-v12-changelog.mdx * Fill SHA-256 checksums for v12.0.1 and v11.7.14 Hash the published Enterprise and Team tarballs. v10.11.25 is still unpublished, so those two checksums stay TBD. Co-authored-by: Amy Blais <[email protected]> * Document the v10.11.25 Go 1.26.10 upgrade The tagged release bumps the runtime from 1.25.8. Record that note and the published Enterprise and Team checksums. Co-authored-by: Amy Blais <[email protected]> * Update mattermost-v10-changelog.mdx --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: Amy Blais <[email protected]>
[MM-71043] Drop IdpMetadataURL from the SAML support packet tests (#39293) The enterprise SAML diagnostic no longer reads IdpMetadataURL. These subtests mock the diagnostic and only exercise the error-to-status mapping, so the metadata-specific failure cases duplicated the generic one.
Clarify when the OnSAMLLogin plugin hook is invoked (#39345)
Make post acknowledgements UpdateAt tests deterministic (#39363) * Replace time.Sleep in post acknowledgements BatchDelete test Co-authored-by: Cursor <[email protected]> * Apply the same UpdateAt rewind to the Save and BatchSave tests Co-authored-by: Cursor <[email protected]> * Read post acknowledgement UpdateAt assertions from master Co-authored-by: Cursor <[email protected]> --------- Co-authored-by: Cursor <[email protected]>
Migrate checkUserPassword from *model.AppError to error. (#39346) The function only returns nil or an AppError it builds itself, plus migratePassword's error after a nil check, so callers no longer need model.AsAppError at this boundary. Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: jesse <[email protected]>
Migrate SectionNotice to Compass UI (#39042) * Migrate SectionNotice to Compass UI adapter Rewrite components/section_notice as a thin adapter over @mattermost/compass-ui/components/section-notice so existing importers keep their legacy props (text, tertiary/link buttons, welcome type). Preserve sectionNoticeContainer type markers for tests and admin SCSS. Update classification notice tests for Compass title semantics and refresh notification notice snapshots. Co-authored-by: Matthew Birtch <[email protected]> * Remove legacy SectionNotice wrapper Co-authored-by: Cursor <[email protected]> * Use Compass SectionNotice directly in all callers Co-authored-by: Cursor <[email protected]> * Fix snapshots and e2e locators for Compass SectionNotice markup Co-authored-by: Cursor <[email protected]> * Use Compass SectionNotice for permission policy info banner Co-authored-by: Cursor <[email protected]> * Update desktop/mobile notifications aria snapshot for Compass SectionNotice Co-authored-by: Cursor <[email protected]> * Use Compass primary actions on danger notification permission notices Tertiary buttons fail WCAG contrast on the danger SectionNotice background. Co-authored-by: Cursor <[email protected]> * Add before/after screenshots for SectionNotice PR Co-authored-by: Cursor <[email protected]> * Remove temporary PR screenshot assets from branch tip Co-authored-by: Cursor <[email protected]> * Add more SectionNotice before/after screenshots for PR Co-authored-by: Cursor <[email protected]> * Remove temporary PR screenshot assets from branch tip Co-authored-by: Cursor <[email protected]> * Add accurate SectionNotice before screenshots from master Capture the pre-migration notice UI from master for PR comparison tables. Co-authored-by: Cursor <[email protected]> * Remove temporary PR screenshot assets from branch tip Co-authored-by: Cursor <[email protected]> * Refresh classification markings before screenshot for PR Recapture the master warning notice without the faded background bleed. Co-authored-by: Cursor <[email protected]> * Remove temporary PR screenshot assets from branch tip Co-authored-by: Cursor <[email protected]> * Use lightbulb icon for troubleshooting notifications notice Compass hint notices default to the info icon; pass LightbulbOutlineIcon explicitly. Co-authored-by: Cursor <[email protected]> * Update send test notification after screenshot with lightbulb icon Co-authored-by: Cursor <[email protected]> * Remove temporary PR screenshot assets from branch tip Co-authored-by: Cursor <[email protected]> * Bump compass-ui to 0.1.0-alpha.16 for SectionNotice heading titles. Restore heading a11y expectations and refresh snapshots for the semantic h4 fix. Co-authored-by: Cursor <[email protected]> * Update Radio snapshots for compass-ui 0.1.0-alpha.16 CSS hashes. The compass-ui bump changes Radio CSS-module class hashes, which broke channels snapshot tests across admin console, settings, and integrations. Co-authored-by: Matthew Birtch <[email protected]> * Bump compass-ui to 0.1.0-alpha.17. Co-authored-by: Cursor <[email protected]> * Bump compass-ui to 0.1.0-alpha.18 for SectionNotice title host margin fix. Co-authored-by: Cursor <[email protected]> * Update SectionNoticeActions snapshot hashes for styled-components 5.3.11 The snapshots were generated against a stale local styled-components 5.3.7, which is hashed into generated class names, so CI (5.3.11) rendered a different class. Co-Authored-By: Claude <[email protected]> --------- Co-authored-by: Cursor Agent <[email protected]> Co-authored-by: Matthew Birtch <[email protected]> Co-authored-by: Claude <[email protected]>
Fix up unusable email settings and translate db command config errors (#39302) * Fix up unusable email settings instead of failing to start v12 validates SupportEmail, FeedbackEmail and ReplyToAddress as a single plain address. #39003 stripped display names, but values that did not parse as one address, such as a list or a bare name, still stopped the server. Keep the first valid address of a list, clear values with none, and log the old value. * Load translations before config in mattermost db commands The db subcommands loaded the config store without loading translations, so a config validation error printed its raw message id instead of a message naming the invalid setting, and the locale check warned that the default "en" locale was unsupported.
Mattermost Security
Mattermost Website
Website
Mattermost | Operational and AI Sovereignty for Critical Infrastructure and National Security
Zero-trust collaboration, automation and AI in private cloud, self-hosted, and air-gapped environments. Built for national security, critical infrastructure, and regulated enterprises.
Redirects
Does not redirect
Security Checks
All 65 security checks passed
Server Details
- IP Address104.18.1.109
- LocationSan Francisco,California,United States of America,NA
- ISPCloudFlare Inc.
- ASNAS13335
Associated Countries
 US
Safety Score
Website marked as safe
100%
Trackers
Loads 2 third-party trackers
- googletagmanager.comGoogle Ads
- qualified.comqualified.com
Blacklist Check
mattermost.com was found on 0 blacklists
- AntiSocial Blacklist
- Artists Against 419
- Badbitcoin
- Bambenek Consulting
- CERT Polska
- CoinBlockerLists
- CRDF
- CryptoScamDB
- EtherAddressLookup
- EtherScamDB
- Fake Website Buster
- MetaMask EthPhishing
- NABP Not Recommended Sites
- OpenPhish
- PetScams
- PhishFeed
- PhishFort
- Phishing.Database
- PhishStats
- PhishTank
- Phishunt
- RPiList Not Serious
- Scam.Directory
- SecureReload Phishing List
- Spam404
- StopGunScams
- Suspicious Hosting IP
- ThreatFox
- ThreatLog
- TweetFeed
- URLhaus
- ViriBack C2 Tracker
Website Preview

Mattermost Android App
APK Info
- AppMattermost
- Creation Date15 Sept 18
- Last Updated19 Jul 24
- Current Version1.11.0
- CreatorMattermost
- Downloads50,000+ downloads
- Privacy ReportView on Exodus →
De-Googled Compatibility
Permissions
- Access Network State
- Camera
- Internet
- Read App Badge
- Read External Storage
- Receive Boot Completed
- System Alert Window
- Use Fingerprint
- Vibrate
- Wake Lock
- Write External Storage
- Update Count
- Receive
- Send
- Read Settings
- Update Shortcut
- Change Badge
- Read Settings
- Write Settings
- Update Badge
- C2d Message
- Read Settings
- Write Settings
- Read
- Write
- Broadcast Badge
- Provider Insert Badge
- Badge Count Read
- Badge Count Write
Mattermost iOS App
App Info
 Mattermost
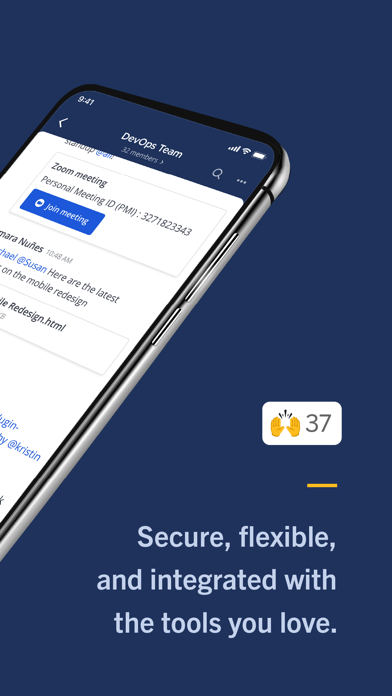
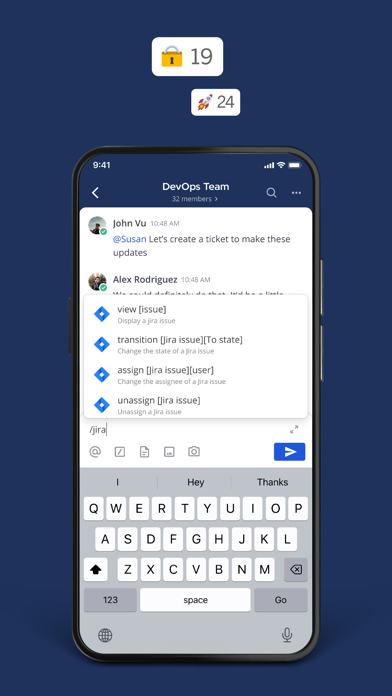
Requires Mattermost Server v11.7.0+. Older servers may not be able to connect or have unexpected behavior. ------- Mattermost is the leading collaborative workflow platform for defense, intelligence, security, and critical infrastructure. The platform runs on-premises and in private clouds, delivering secure messaging, file sharing, workflow automation, audio/screenshare, and project management—all with full data and operational control. - Securely share messages, files, and links across from your preferred mobile devices. - Start 1:1 and group voice calls with a single click without leaving Mattermost. - Keep critical workflows moving forward with Playbook. - Get the message out without having to manage every endpoint with Enterprise Mobility Management (AppConfig) support. - Private mobility with ID-only push notifications to keep sensitive data protected while keeping stakeholders informed. To use this app, you need a URL for a Mattermost server. ------- Deploy your own server: https://docs.mattermost.com/guides/deployment.html Terms of Service: https://mattermost.com/terms-of-service/ Contribute to the project: https://github.com/mattermost/mattermost-mobile
Rating
Version Info
- Current Version2.44.0
- Last Updated16 Sept 26
- First Released10 Jul 17
- Minimum iOS Version16.0
- Device Models Supported130
App Details
- IPA Size93.41 Mb
- PriceFree (USD)
- Age Advisory4+
- Supported Languages21
- DeveloperMattermost, Inc.
- Bundle IDcom.mattermost.rn
Screenshots

Mattermost Docker
Container Info
 mattermost
Mattermost - open-source team chat: channels, threads, DMs, voice calls, slash commands, integrations, and plugins. Team Edition image on a managed Postgres - it listens on :5000 directly, so no proxy.
Run Command
docker run -d \
  -e MM_SITE_URL=${MM_SITE_URL} \
Compose File
version: 3.8
services:
  mattermost:
    environment:
      MM_SITE_URL: "http://localhost:5000"
Environment Variables
- Var NameDefault
- MM_SITE_URLhttp://localhost:5000
Mattermost Reviews
More Team Collaboration
Privacy-focused messenger using the Matrix protocol. The Element client allows for group chat rooms, media sharing, voice and video group calls. End-to-end encryption by default for message content, but not metadata, which remains visible to the home server operator.
Easy-to-deploy, self-hosted Slack alternative with polished cross-platform apps. End-to-end encryption is supported, but off by default - without it, workspace admins can read all messages. Usage statistics are sent by default.
A decentralized, encrypted P2P friend-to-friend app for chat, forums, channels, boards, voice calls and anonymous file sharing. Best for trusted contacts, as it isn't anonymous unless you route it through Tor (off by default).
Open source team chat organized around topic-based threading, which keeps busy conversations easier to follow than channel-only tools. Can be self-hosted, or used as a paid cloud service. The threading model takes some getting used to.



About the Data: Mattermost
Change History
- Amended (description, openSource, url) #770
- Amended (androidApp, iosApp)
Edit Mattermost Data
You can edit Mattermost's entry in this section of awesome-privacy.yml by submitting a PR to our GitHub repo.
Note that some of the information shown above has been aggregated from external
sources, a list of these can be found data documentation.
Origin Data
Modify Data
API
You can access Mattermost's data programmatically via our API. Simply make a GET request to:
https://api.awesome-privacy.xyz/v1/services/mattermostThe REST API is free, no-auth and CORS-enabled. To learn more, view the API Docs or read the API Usage Guide.
Share Mattermost
Help your friends compare Team Collaboration, and pick privacy-respecting software and services.
Share Mattermost and Awesome Privacy with your network!