Ente Photos
ente.comSelf-hosted
Provides an open source, audited end-to-end encrypted platform to store photos in the cloud without needing to trust the service provider. With apps for desktop, web and mobile, album sharing, public links, semantic search and facial recognition. Self-hosted or 10GB free.
- Homepage:ente.com
- GitHub:github.com/ente-io/ente
- iOS App:apps.apple.com/us/app/ente-photos/id1542026904
- Android App:play.google.com/.../io.ente.photos
- Discord:z2YVKkycX3
- Subreddit:r/enteio
- Web info:web-check.xyz/check/ente.com
Ente Photos Source Code
Author

Description
💚 End-to-end encrypted cloud for everything.
Homepage
https://ente.comRepository
- LicenseAGPL-3.0
- Created01 Nov 22
- Primary languageDart
- Size729,133 KB
- Stars28,636
- Forks1,780
- Watchers28,636
Top Contributors
@mnvr (13252)
@ua741 (11095)
@abhinavkgrd (9347)
@ashilkn (5649)
@vishnukvmd (4662)
@laurenspriem (3807)
@prateekmedia (2707)
@AmanRajSinghMourya (2318)
@anandbaburajan (1604)
@AswinAsok (1136)
@crowdin-bot (777)
@aspizu (398)
@Shanthy17 (288)
@rushitote (281)
@httpjamesm (250)
@mngshm (195)
@aman-pilot (170)
@pushkar8723 (168)
@shaileshpandit (157)
@Amrithesh-Kakkoth (149)
@Ananddubey01 (124)
@jubitjohn (120)
@github-actions[bot] (79)
@ashil-pilot (76)
@neeraj-pilot (68)
@grittypuffy (67)
@i-aiymen (63)
@dependabot[bot] (54)
@setalp (51)
@claude (47)
@tanguylegazon (35)
@r4khul (33)
@atyabbin (33)
@ente-ci[bot] (32)
@a5xwin (31)
@Jishnuraj9 (30)
@sv3nnie (24)
@slisaasquatch (23)
@greeeen-dev (21)
@megaberry (20)
@Muhesh7 (19)
@karayelxyz (18)
@Ashton20271 (17)
@desaianand1 (17)
@fosszil (17)
@JamsRepos (16)
@vs704vs (15)
@Bl4ckspell7 (15)
@simondubrulle (14)
@brog-io (14)
@eYdr1en (12)
@nikunjkumarnakum (11)
@4fosaefp (11)
@ivnnv (10)
@NylaTheWolf (10)
@vbenincasa (10)
@ialexanderbrito (10)
@codebydant (9)
@Dizzy-DB (8)
@JacquesLucke (8)
@Ranhiru (8)
@TomsDex (7)
@chmromano (6)
@facundosterzerforino (6)
@jake-anto (6)
@m7moud (6)
@SpoonySimone (6)
@millia-rage (6)
@laurens-pilot (6)
@0nullpointer (6)
@tristan-derez (5)
@Copilot (5)
@jaashuu (5)
@ludespeedny (5)
@pixelGoblin (5)
@Trekky12 (5)
@k3kk07 (5)
@zDqrK404 (5)
@ShivamHP (5)
@shinebayar-g (5)
@RAJP81 (5)
@lyonelf (5)
@Apalepex (5)
@kingluc12 (5)
@fco-pires (5)
@jincao1 (4)
@Naveenchand06 (4)
@iedame (4)
@pashynskykh (4)
@AlexMicael (4)
@slacker-treat-deferred-unbuckled-jiffy (4)
@dunny1g (4)
@casualsailo (4)
@ballingbyte (4)
@stantios (4)
@StDensity (4)
@shmshd (4)
@NanoBunTV (4)
@Hamster45105 (4)
@erannave (4)
Recent Commits
[desktop][photos] Support XMP sidecars for uploads (#12585)
[mob][photos] Create Uncategorized album during sync (#12594) ## What Create the Uncategorized album during collection sync instead of when it is first opened. ## Testing Tested with a new account in the iOS Simulator. Verified the album is created before opening More and opens successfully.
[mob][photos] Add Uncategorized fix changelog
[mob][photos] Align Uncategorized failure log
minor-content-correction
[mob][photos] Clarify Uncategorized ensure helper
[mob][photos] Remove redundant sync comment
chore(xmp):add-internalUser-flag
[mob][photos] Rely on server for Uncategorized uniqueness
[desktop][photos] Fix desktop HLS failures persist the account session token in logs (#12589)
[infra] Consolidate change approval gate (#12595)
[rust] Route Locker account crypto through its WASM artifact (#12593)
Consolidate workflow security checks
Simplify change approval workflow
[mob][photos] Simplify Uncategorized lookup
update-changes
fix(metadata-json):fix-XMP-location-parsing-issue
[mob][photos] Ensure Uncategorized album after sync
Route Locker account crypto through its WASM artifact Bind session and account-key decryption in Locker's service composition so ordinary reads no longer select Core through Accounts helpers. Keep existing Core consumers behind a small temporary adapter. Share the interactive KDF projection in ente-wasm-lib and expose it through Locker's wrapper-owned worker. Copy and free GeneratedKek values using readonly camelCase getters while retaining Core's TypeScript API. The KDF worker uses direct Comlink transport, as Paste does. Rust logs use the console fallback instead of the Accounts worker's persisted-log bridge.
Bump @xmldom/xmldom from 0.9.10 to 0.9.12 in /web in the web-security group across 1 directory (#12577) Bumps the web-security group with 1 update in the /web directory: [@xmldom/xmldom](https://github.com/xmldom/xmldom). Updates `@xmldom/xmldom` from 0.9.10 to 0.9.12 <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/xmldom/xmldom/releases">@xmldom/xmldom's releases</a>.</em></p> <blockquote> <h2>0.9.12</h2> <p><a href="https://github.com/xmldom/xmldom/compare/0.9.11...0.9.12">Commits</a></p> <h3>Fixed</h3> <ul> <li>Security: parsing a deeply or repeatedly namespaced document no longer consumes quadratic memory; the in-scope namespace map is inherited through the prototype chain instead of being copied for every prefix-declaring element (O(N) instead of O(N²)), preventing a denial-of-service reachable from <code>DOMParser.parseFromString</code> with default options. Serialized output is byte-identical. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-965w-775f-mr7g"><code>GHSA-965w-775f-mr7g</code></a></li> <li>Security: attribute de-duplication during parsing is now O(M) instead of O(M²); the <code>NamedNodeMap</code> parse-time dedup path uses a null-prototype membership index, so a well-formed document with a hostile number of duplicate attributes can no longer wedge the parse. Attribute order and duplicate resolution (last value wins, first position kept) are byte-identical, preserving the XML <a href="https://www.w3.org/TR/xml/#uniqattspec">no-duplicate-attributes well-formedness constraint</a>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-8344-3jmq-59r6"><code>GHSA-8344-3jmq-59r6</code></a></li> <li>Security: HTML raw-text parsing no longer amplifies output on a missing or case-mismatched closing tag; the closing tag is matched case-insensitively per the WHATWG HTML <a href="https://html.spec.whatwg.org/multipage/parsing.html#rawtext-end-tag-name-state">RAWTEXT end-tag rule</a> and a missing closing tag is handled explicitly, preventing a denial-of-service. Output for well-formed input is unchanged. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6mj3-qw4j-hgrw"><code>GHSA-6mj3-qw4j-hgrw</code></a></li> <li>Security: malformed-input recovery is now linear instead of quadratic — the malformed tag-name scan terminates at an embedded <code><</code>, and <code>Node.prototype.normalize()</code> merges adjacent text nodes in O(K) instead of O(K²) (also reachable programmatically), per <a href="https://dom.spec.whatwg.org/#dom-node-normalize"><code>normalize()</code></a> in the WHATWG DOM spec. DOM output is unchanged; only the reported error text differs. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-93r5-fhx6-vmg9"><code>GHSA-93r5-fhx6-vmg9</code></a></li> <li>Security: <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> now rejects a DocType <code>name</code> that is not a valid XML <a href="https://www.w3.org/TR/xml/#NT-Name"><code>Name</code></a>, throwing <code>InvalidStateError</code> — matching the sibling <code>publicId</code>/<code>systemId</code>/<code>internalSubset</code> checks and preventing XML injection via <code>DocumentType.name</code>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-27p8-2357-5qqv"><code>GHSA-27p8-2357-5qqv</code></a></li> <li>Security: <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> now validates a processing-instruction target as an XML <a href="https://www.w3.org/TR/xml-names/#NT-NCName"><code>NCName</code></a> and rejects a case-insensitive <code>xml</code>, throwing <code>InvalidStateError</code> — preventing PI-target injection via <code>></code>, <code>?</code>, or whitespace. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-c7q8-3ch8-vqpv"><code>GHSA-c7q8-3ch8-vqpv</code></a></li> <li>Security: <code>Document.createEntityReference()</code> now rejects an invalid XML <a href="https://www.w3.org/TR/xml/#NT-Name"><code>Name</code></a> at creation, and <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> validates an <code>EntityReference</code> <code>nodeName</code> as an XML <code>Name</code>, throwing <code>InvalidStateError</code> — preventing XML injection via an entity-reference name. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6gmq-8vp8-gcm6"><code>GHSA-6gmq-8vp8-gcm6</code></a></li> <li>Security: the <code>requireWellFormed</code> serializer's element- and attribute-name validators no longer treat an interior line terminator as satisfying the name anchors, so a name containing a line terminator is rejected with <code>InvalidStateError</code> — closing a bypass of the XML <a href="https://www.w3.org/TR/xml-names/#NT-QName"><code>QName</code></a> check. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-jxjr-3g7g-3944"><code>GHSA-jxjr-3g7g-3944</code></a></li> <li>Security: the <code>requireWellFormed</code> serializer's DocType <code>publicId</code>/<code>systemId</code> validators no longer treat an interior line terminator as satisfying the anchor, so an identifier containing an ECMAScript line terminator is rejected with <code>InvalidStateError</code> — closing a bypass of the XML <a href="https://www.w3.org/TR/xml/#NT-PubidLiteral"><code>PubidLiteral</code></a>/<code>SystemLiteral</code> check. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-vr34-hp96-76pp"><code>GHSA-vr34-hp96-76pp</code></a></li> <li>Security: <code>createElementNS()</code>, <code>createAttributeNS()</code>, <code>createDocumentType()</code>, and <code>createAttribute()</code> now reject a name containing a line terminator with <code>InvalidCharacterError</code>, because name validation applies to the whole string — closing a creation-time bypass of the XML <a href="https://www.w3.org/TR/xml-names/#NT-QName"><code>Name</code>/<code>QName</code></a> production on the default serialization path. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-3px3-54cx-rmw9"><code>GHSA-3px3-54cx-rmw9</code></a></li> <li>Security: the parser now reports a not-well-formed end tag whose valid name is followed by trailing content (a recoverable <code>error</code> in XML, a <code>warning</code> in HTML) instead of accepting it silently, per the XML <a href="https://www.w3.org/TR/xml/#NT-ETag"><code>ETag</code></a> production; parsing recovers to the byte-identical DOM. Consumers that want strict rejection can escalate the reported <code>error</code> to fatal via the parser's <code>onError</code> handler. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6h8r-xr42-gp59"><code>GHSA-6h8r-xr42-gp59</code></a></li> <li><code>DOMException</code>s raised during parsing are now reported as a <code>fatalError</code>, and the originating error is preserved as the <code>cause</code> on the resulting <code>ParseError</code>.</li> </ul> <h3>Chore</h3> <ul> <li>updated dependencies</li> </ul> <p>Thank you, <a href="https://github.com/ericchiang"><code>@ericchiang</code></a>, <a href="https://github.com/KarimTantawey"><code>@KarimTantawey</code></a>, <a href="https://github.com/bhaswanthc"><code>@bhaswanthc</code></a>, <a href="https://github.com/arpitjain099"><code>@arpitjain099</code></a>, <a href="https://github.com/Paranoidgrinch"><code>@Paranoidgrinch</code></a>, for your contributions</p> <h2>0.9.11</h2> <p><a href="https://github.com/xmldom/xmldom/compare/0.9.10...0.9.11">Commits</a></p> <h3>Fixed</h3> <ul> <li>Security: <code>XMLSerializer.serializeToString()</code> now also rejects invalid element and attribute names when <code>{ requireWellFormed: true }</code> is passed, throwing <code>InvalidStateError</code> for a name that is not a valid XML <a href="https://www.w3.org/TR/xml-names/#NT-QName"><code>QName</code></a> (this covers the namespace prefix, which surfaces in the element qualified name or in a synthesized <code>xmlns:</code> declaration). This prevents XML injection via <code>createElement()</code> / <code>setAttribute()</code>, extending the existing <code>requireWellFormed</code> checks to the serialized name set. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-w2rr-34g9-rvrj"><code>GHSA-w2rr-34g9-rvrj</code></a> <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-4w3w-2rp5-g8jm"><code>GHSA-4w3w-2rp5-g8jm</code></a></li> <li>Security: the processing-instruction grammar regex no longer backtracks quadratically on an unterminated processing instruction (<code><?…</code> with no closing <code>?></code>), preventing a denial-of-service (ReDoS) reachable from <code>DOMParser.parseFromString</code> with default options. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-g53g-w8rj-fmg7"><code>GHSA-g53g-w8rj-fmg7</code></a></li> <li><code>CharacterData</code> <code>nodeValue</code> and <code>data</code> are now kept in sync <a href="https://redirect.github.com/xmldom/xmldom/pull/990"><code>[#990](https://github.com/xmldom/xmldom/issues/990)</code></a></li> </ul> <h3>Chore</h3> <ul> <li>updated dependencies</li> </ul> <p>Thank you, <a href="https://github.com/bhaswanthc"><code>@bhaswanthc</code></a>, <a href="https://github.com/jmestwa-coder"><code>@jmestwa-coder</code></a>, <a href="https://github.com/stevenobiajulu"><code>@stevenobiajulu</code></a>, for your contributions</p> </blockquote> </details> <details> <summary>Changelog</summary> <p><em>Sourced from <a href="https://github.com/xmldom/xmldom/blob/master/CHANGELOG.md">@xmldom/xmldom's changelog</a>.</em></p> <blockquote> <h2><a href="https://github.com/xmldom/xmldom/compare/0.9.11...0.9.12">0.9.12</a></h2> <h3>Fixed</h3> <ul> <li>Security: parsing a deeply or repeatedly namespaced document no longer consumes quadratic memory; the in-scope namespace map is inherited through the prototype chain instead of being copied for every prefix-declaring element (O(N) instead of O(N²)), preventing a denial-of-service reachable from <code>DOMParser.parseFromString</code> with default options. Serialized output is byte-identical. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-965w-775f-mr7g"><code>GHSA-965w-775f-mr7g</code></a></li> <li>Security: attribute de-duplication during parsing is now O(M) instead of O(M²); the <code>NamedNodeMap</code> parse-time dedup path uses a null-prototype membership index, so a well-formed document with a hostile number of duplicate attributes can no longer wedge the parse. Attribute order and duplicate resolution (last value wins, first position kept) are byte-identical, preserving the XML <a href="https://www.w3.org/TR/xml/#uniqattspec">no-duplicate-attributes well-formedness constraint</a>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-8344-3jmq-59r6"><code>GHSA-8344-3jmq-59r6</code></a></li> <li>Security: HTML raw-text parsing no longer amplifies output on a missing or case-mismatched closing tag; the closing tag is matched case-insensitively per the WHATWG HTML <a href="https://html.spec.whatwg.org/multipage/parsing.html#rawtext-end-tag-name-state">RAWTEXT end-tag rule</a> and a missing closing tag is handled explicitly, preventing a denial-of-service. Output for well-formed input is unchanged. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6mj3-qw4j-hgrw"><code>GHSA-6mj3-qw4j-hgrw</code></a></li> <li>Security: malformed-input recovery is now linear instead of quadratic — the malformed tag-name scan terminates at an embedded <code><</code>, and <code>Node.prototype.normalize()</code> merges adjacent text nodes in O(K) instead of O(K²) (also reachable programmatically), per <a href="https://dom.spec.whatwg.org/#dom-node-normalize"><code>normalize()</code></a> in the WHATWG DOM spec. DOM output is unchanged; only the reported error text differs. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-93r5-fhx6-vmg9"><code>GHSA-93r5-fhx6-vmg9</code></a></li> <li>Security: <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> now rejects a DocType <code>name</code> that is not a valid XML <a href="https://www.w3.org/TR/xml/#NT-Name"><code>Name</code></a>, throwing <code>InvalidStateError</code> — matching the sibling <code>publicId</code>/<code>systemId</code>/<code>internalSubset</code> checks and preventing XML injection via <code>DocumentType.name</code>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-27p8-2357-5qqv"><code>GHSA-27p8-2357-5qqv</code></a></li> <li>Security: <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> now validates a processing-instruction target as an XML <a href="https://www.w3.org/TR/xml-names/#NT-NCName"><code>NCName</code></a> and rejects a case-insensitive <code>xml</code>, throwing <code>InvalidStateError</code> — preventing PI-target injection via <code>></code>, <code>?</code>, or whitespace. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-c7q8-3ch8-vqpv"><code>GHSA-c7q8-3ch8-vqpv</code></a></li> <li>Security: <code>Document.createEntityReference()</code> now rejects an invalid XML <a href="https://www.w3.org/TR/xml/#NT-Name"><code>Name</code></a> at creation, and <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> validates an <code>EntityReference</code> <code>nodeName</code> as an XML <code>Name</code>, throwing <code>InvalidStateError</code> — preventing XML injection via an entity-reference name. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6gmq-8vp8-gcm6"><code>GHSA-6gmq-8vp8-gcm6</code></a></li> <li>Security: the <code>requireWellFormed</code> serializer's element- and attribute-name validators no longer treat an interior line terminator as satisfying the name anchors, so a name containing a line terminator is rejected with <code>InvalidStateError</code> — closing a bypass of the XML <a href="https://www.w3.org/TR/xml-names/#NT-QName"><code>QName</code></a> check. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-jxjr-3g7g-3944"><code>GHSA-jxjr-3g7g-3944</code></a></li> <li>Security: the <code>requireWellFormed</code> serializer's DocType <code>publicId</code>/<code>systemId</code> validators no longer treat an interior line terminator as satisfying the anchor, so an identifier containing an ECMAScript line terminator is rejected with <code>InvalidStateError</code> — closing a bypass of the XML <a href="https://www.w3.org/TR/xml/#NT-PubidLiteral"><code>PubidLiteral</code></a>/<code>SystemLiteral</code> check. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-vr34-hp96-76pp"><code>GHSA-vr34-hp96-76pp</code></a></li> <li>Security: <code>createElementNS()</code>, <code>createAttributeNS()</code>, <code>createDocumentType()</code>, and <code>createAttribute()</code> now reject a name containing a line terminator with <code>InvalidCharacterError</code>, because name validation applies to the whole string — closing a creation-time bypass of the XML <a href="https://www.w3.org/TR/xml-names/#NT-QName"><code>Name</code>/<code>QName</code></a> production on the default serialization path. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-3px3-54cx-rmw9"><code>GHSA-3px3-54cx-rmw9</code></a></li> <li>Security: the parser now reports a not-well-formed end tag whose valid name is followed by trailing content (a recoverable <code>error</code> in XML, a <code>warning</code> in HTML) instead of accepting it silently, per the XML <a href="https://www.w3.org/TR/xml/#NT-ETag"><code>ETag</code></a> production; parsing recovers to the byte-identical DOM. Consumers that want strict rejection can escalate the reported <code>error</code> to fatal via the parser's <code>onError</code> handler. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6h8r-xr42-gp59"><code>GHSA-6h8r-xr42-gp59</code></a></li> <li><code>DOMException</code>s raised during parsing are now reported as a <code>fatalError</code>, and the originating error is preserved as the <code>cause</code> on the resulting <code>ParseError</code>.</li> </ul> <h3>Chore</h3> <ul> <li>updated dependencies</li> </ul> <p>Thank you, <a href="https://github.com/ericchiang"><code>@ericchiang</code></a>, <a href="https://github.com/KarimTantawey"><code>@KarimTantawey</code></a>, <a href="https://github.com/bhaswanthc"><code>@bhaswanthc</code></a>, <a href="https://github.com/arpitjain099"><code>@arpitjain099</code></a>, <a href="https://github.com/Paranoidgrinch"><code>@Paranoidgrinch</code></a>, for your contributions</p> <h2><a href="https://github.com/xmldom/xmldom/compare/0.8.14...0.8.15">0.8.15</a></h2> <h3>Fixed</h3> <ul> <li>Security: parsing a deeply or repeatedly namespaced document no longer consumes quadratic memory; the in-scope namespace map is inherited through the prototype chain instead of being copied for every prefix-declaring element (O(N) instead of O(N²)), preventing a denial-of-service reachable from <code>DOMParser.parseFromString</code> with default options. Serialized output is byte-identical. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-965w-775f-mr7g"><code>GHSA-965w-775f-mr7g</code></a></li> <li>Security: attribute de-duplication during parsing is now O(M) instead of O(M²); the <code>NamedNodeMap</code> parse-time dedup path uses a null-prototype membership index, so a well-formed document with a hostile number of duplicate attributes can no longer wedge the parse. Attribute order and duplicate resolution (last value wins, first position kept) are byte-identical, preserving the XML <a href="https://www.w3.org/TR/xml/#uniqattspec">no-duplicate-attributes well-formedness constraint</a>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-8344-3jmq-59r6"><code>GHSA-8344-3jmq-59r6</code></a></li> <li>Security: trimming trailing whitespace from an XML end tag (<a href="https://www.w3.org/TR/xml/#NT-ETag"><code>ETag</code></a>) is now anchored so it runs in linear time instead of backtracking quadratically on a long whitespace run, preventing a ReDoS reachable from <code>DOMParser.parseFromString</code>. Trimmed output is byte-identical. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-x4fp-j954-r2f4"><code>GHSA-x4fp-j954-r2f4</code></a></li> <li>Security: malformed-input recovery is now linear instead of quadratic — the malformed tag-name scan terminates at an embedded <code><</code>, and <code>Node.prototype.normalize()</code> merges adjacent text nodes in O(K) instead of O(K²) (also reachable programmatically), per <a href="https://dom.spec.whatwg.org/#dom-node-normalize"><code>normalize()</code></a> in the WHATWG DOM spec. DOM output is unchanged; only the reported error text differs. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-93r5-fhx6-vmg9"><code>GHSA-93r5-fhx6-vmg9</code></a></li> <li>Security: <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> now rejects a DocType <code>name</code> that is not a valid XML <a href="https://www.w3.org/TR/xml/#NT-Name"><code>Name</code></a>, throwing <code>InvalidStateError</code> — matching the sibling <code>publicId</code>/<code>systemId</code>/<code>internalSubset</code> checks and preventing XML injection via <code>DocumentType.name</code>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-27p8-2357-5qqv"><code>GHSA-27p8-2357-5qqv</code></a></li> <li>Security: <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> now validates a processing-instruction target as an XML <a href="https://www.w3.org/TR/xml-names/#NT-NCName"><code>NCName</code></a> and rejects a case-insensitive <code>xml</code>, throwing <code>InvalidStateError</code> — a check <code>0.8.x</code> did not previously perform, preventing PI-target injection via <code>></code>, <code>?</code>, or whitespace. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-c7q8-3ch8-vqpv"><code>GHSA-c7q8-3ch8-vqpv</code></a></li> <li>Security: <code>Document.createEntityReference()</code> now rejects an invalid XML <a href="https://www.w3.org/TR/xml/#NT-Name"><code>Name</code></a> at creation, and <code>XMLSerializer.serializeToString()</code> under <code>{ requireWellFormed: true }</code> validates an <code>EntityReference</code> <code>nodeName</code> as an XML <code>Name</code>, throwing <code>InvalidStateError</code> — preventing XML injection via an entity-reference name. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6gmq-8vp8-gcm6"><code>GHSA-6gmq-8vp8-gcm6</code></a></li> <li>Security: the parser now reports a not-well-formed end tag whose valid name is followed by trailing content as a recoverable <code>error</code> instead of accepting it silently, per the XML <a href="https://www.w3.org/TR/xml/#NT-ETag"><code>ETag</code></a> production; parsing recovers to the byte-identical DOM. Consumers that want strict rejection can escalate the reported <code>error</code> to fatal via the parser's <code>errorHandler</code>. <a href="https://github.com/xmldom/xmldom/security/advisories/GHSA-6h8r-xr42-gp59"><code>GHSA-6h8r-xr42-gp59</code></a></li> </ul> <p>Thank you, <a href="https://github.com/ericchiang"><code>@ericchiang</code></a>, <a href="https://github.com/bhaswanthc"><code>@bhaswanthc</code></a>, <a href="https://github.com/arpitjain099"><code>@arpitjain099</code></a>, <a href="https://github.com/Paranoidgrinch"><code>@Paranoidgrinch</code></a>, for your contributions</p> <h2><a href="https://github.com/xmldom/xmldom/compare/0.9.10...0.9.11">0.9.11</a></h2> <!-- raw HTML omitted --> </blockquote> <p>... (truncated)</p> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/xmldom/xmldom/commit/0af8cf829d8a92bbac612903422c6947f5458f06"><code>0af8cf8</code></a> 0.9.12</li> <li><a href="https://github.com/xmldom/xmldom/commit/69d257bd677aed2dde833a6dd67ddf244c370e41"><code>69d257b</code></a> docs: add 0.9.12 CHANGELOG entry</li> <li><a href="https://github.com/xmldom/xmldom/commit/e53e9b125de830559747b09d9f152c255600ddb9"><code>e53e9b1</code></a> docs: add 0.8.15 CHANGELOG entry</li> <li><a href="https://github.com/xmldom/xmldom/commit/0748720b620555f8c222782dcab575cf0cf403b4"><code>0748720</code></a> fix: prevent quadratic malformed-tag recovery and normalize() adjacent-text m...</li> <li><a href="https://github.com/xmldom/xmldom/commit/7ced40c06c28d151e996a97045018c3559ae4707"><code>7ced40c</code></a> fix: prevent HTML raw-text output amplification via case-insensitive close-ta...</li> <li><a href="https://github.com/xmldom/xmldom/commit/cfb09b5dbeb035fdfedc9f01e2bbaf226bf47cf3"><code>cfb09b5</code></a> fix: prevent quadratic attribute de-duplication via null-prototype membership...</li> <li><a href="https://github.com/xmldom/xmldom/commit/e9dbc6b54c4a9fa83e678647bc1544a505522040"><code>e9dbc6b</code></a> test: characterize NamedNodeMap attribute de-duplication before the index ref...</li> <li><a href="https://github.com/xmldom/xmldom/commit/dabffe884e864eeecb1f515c716f875e1bc47ec1"><code>dabffe8</code></a> fix: prevent quadratic namespace-map memory consumption via prototype-chain i...</li> <li><a href="https://github.com/xmldom/xmldom/commit/7b2ec67e1750daadd0bb06c92e875e726544a362"><code>7b2ec67</code></a> fix: prevent multiline-anchor bypass of name/id validation by dropping the re...</li> <li><a href="https://github.com/xmldom/xmldom/commit/4664386e4f4d99d17b416a151dbe8323e245284b"><code>4664386</code></a> fix: prevent XML injection via unsafe EntityReference name (GHSA-6gmq-8vp8-gcm6)</li> <li>Additional commits viewable in <a href="https://github.com/xmldom/xmldom/compare/0.9.10...0.9.12">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~karfau">karfau</a>, a new releaser for <code>@xmldom/xmldom</code> since your current version.</p> </details> <br />
[server] Require existing usage rows for updates (#12590)
fix(stream):handle-options-request
Require existing usage rows for updates
Bump @xmldom/xmldom in /web in the web-security group across 1 directory Bumps the web-security group with 1 update in the /web directory: [@xmldom/xmldom](https://github.com/xmldom/xmldom). Updates `@xmldom/xmldom` from 0.9.10 to 0.9.12 - [Release notes](https://github.com/xmldom/xmldom/releases) - [Changelog](https://github.com/xmldom/xmldom/blob/master/CHANGELOG.md) - [Commits](https://github.com/xmldom/xmldom/compare/0.9.10...0.9.12) --- updated-dependencies: - dependency-name: "@xmldom/xmldom" dependency-version: 0.9.12 dependency-type: indirect dependency-group: web-security ... Signed-off-by: dependabot[bot] <[email protected]>
[rust] Move Locker crypto into its WASM artifact (#12587)
[infra] Organize repository checks and improve binary change approval (#12588)
add-test
fix(stream):pass-token-in-header
fix(metadata-json):fix-wrapperless-sidecar-parsing
Group repository checks by capability Move standalone checks and their tests under scoped checks directories. Update callers and relative roots, and preserve approval coverage for the relocated guardrails. Trusted-checker jobs use only the new paths and will fail when the PR base still has the old paths.
Ente Photos Security
Security Advisories (2)
- highPatchedCVSS 7.1
GHSA-2hxj-953x-c2vwAccepted emergency contact can bypass the recovery notice period
- mediumPatched
CVE-2026-732302of3 cards v1 contain a checksum that enables offline guessing of low-entropy secrets
Ente Photos Website
Website
Ente Photos: Store and share your photos with absolute privacy
Ente Photos is the private, secure photo storage app with end-to-end encryption. Cross-platform, open source, and self-hostable. Start with 10GB free.
Redirects
Does not redirect
Security Checks
All 65 security checks passed
Server Details
- IP Address172.66.152.229
- LocationSan Francisco,California,United States of America,NA
- ISPCloudFlare Inc.
- ASNAS13335
Associated Countries
 US
Safety Score
Website marked as safe
100%
Blacklist Check
ente.com was found on 0 blacklists
- AntiSocial Blacklist
- Artists Against 419
- Badbitcoin
- Bambenek Consulting
- CERT Polska
- CoinBlockerLists
- CRDF
- CryptoScamDB
- EtherAddressLookup
- EtherScamDB
- Fake Website Buster
- MetaMask EthPhishing
- NABP Not Recommended Sites
- OpenPhish
- PetScams
- PhishFeed
- PhishFort
- Phishing.Database
- PhishStats
- PhishTank
- Phishunt
- RPiList Not Serious
- Scam.Directory
- SecureReload Phishing List
- Spam404
- StopGunScams
- Suspicious Hosting IP
- ThreatFox
- ThreatLog
- TweetFeed
- URLhaus
- ViriBack C2 Tracker
Website Preview

Ente Photos Android App
APK Info
- Appente Photos
- Creation Date12 May 24
- Last Updated14 Jul 24
- Current Version0.8.94
- Privacy ReportView on Exodus →
De-Googled Compatibility
- GrapheneOSNative4.0 / 4(7)
- Project Infinity XmicroG4.0 / 4(2)
Permissions
- Access Media Location
- Access Network State
- Foreground Service
- Internet
- Manage Media
- Post Notifications
- Read External Storage
- Read Media Images
- Read Media Video
- Receive Boot Completed
- Schedule Exact Alarm
- Set Wallpaper
- Use Biometric
- Use Fingerprint
- Vibrate
- Wake Lock
- Write External Storage
- Billing
- Receive
- Dynamic Receiver Not Exported Permission
Ente Photos iOS App
App Info
 Ente Photos
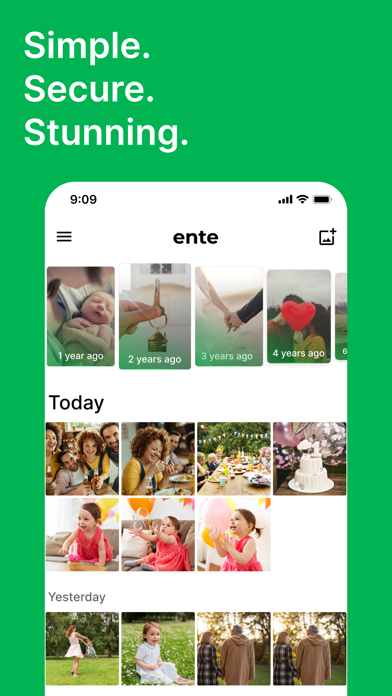
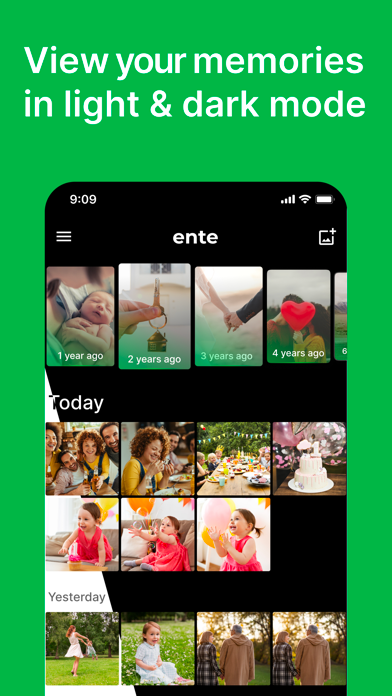
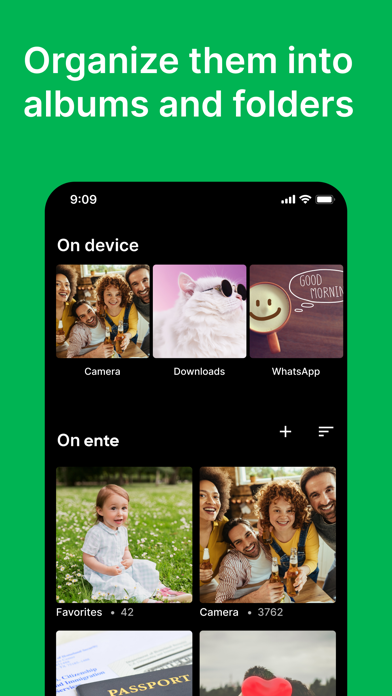
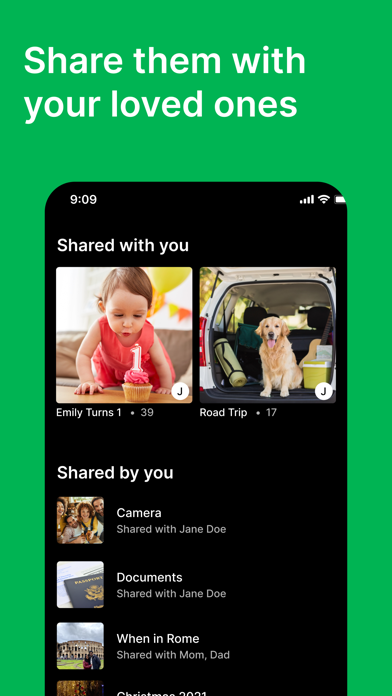
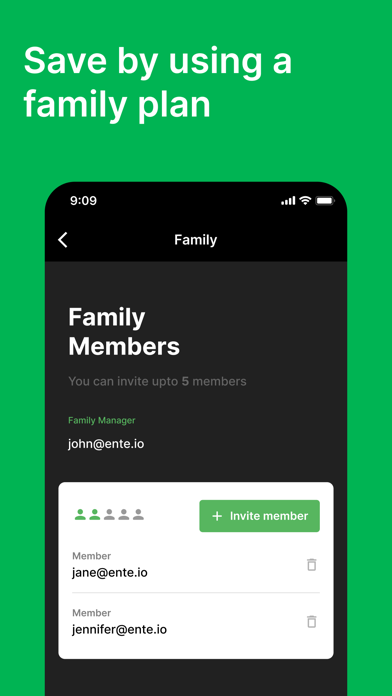
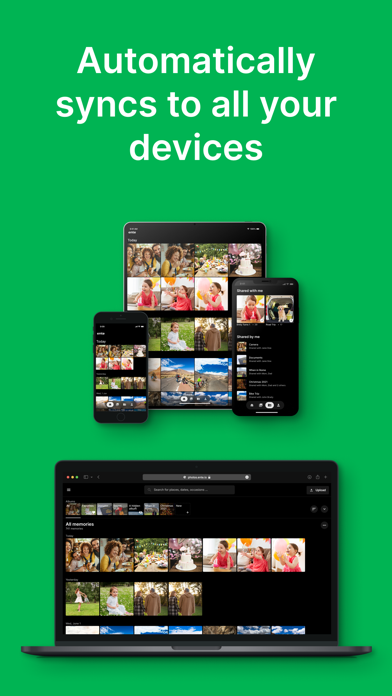
Store, share and discover your memories with Ente Photos. With end-to-end encryption, only you — and those you share with — can see your photos and videos. Ente Photos has lovingly protected over 165 million memories for people who trust us across all major platforms. Get started with 10 GB free. Why Ente Photos? Ente Photos is designed for those who truly value their memories. With end-to-end encryption and secure backups in three locations, your photos stay truly private and safe. Powerful on-device AI helps you find faces and objects instantly, while curated stories bring cherished memories to the present. Share encrypted albums with loved ones, invite family at no extra cost, and lock sensitive images with a password. Available on mobile, desktop, and web, Ente preserves every pixel of your photos and videos. Features: END-TO-END ENCRYPTED STORAGE: Your photos and videos are encrypted on your device, and then automatically backed up to the cloud. SHARE AND COLLABORATE: Let your family or friends add photos and videos to your albums. Everything, end-to-end encrypted. RELIVE YOUR MEMORIES: Through the stories Ente curates for you, relive your memories from previous years. Easily spread the cheer by sharing them with your loved ones or friends. SEARCH FOR ANYONE AND ANYTHING: Using on-device AI, Ente helps you find faces and key elements in a photo, so you can search through your entire library using natural language search. INVITE YOUR FAMILY: Invite up to 5 family members to any paid plan at no extra cost. Only your storage space is shared, not your data. Each member will receive their own private space. AVAILABLE EVERYWHERE: Ente Photos is available on every platform, so you can access your photos and videos from any device you have. NEVER LOSE YOUR PHOTOS: Ente stores your encrypted backups in 3 secure locations—including an underground facility—so your photos stay safe, no matter what. EASY IMPORT: Use our powerful desktop app to import data from other providers. If you need any help moving, reach out, and we'll be there. ORIGINAL QUALITY BACKUPS: All photos and videos are stored in their original quality, including the metadata, without any compression or loss in quality. APP LOCK: Make sure no one else can see your photos and videos using the built in App Lock. You can set a pin, or use biometrics to lock the app only for yourself. HIDDEN PHOTOS: Hide your most private photos and videos to the Hidden folder, which is password protected by default. FREE DEVICE SPACE: Free up your device's space by clearing files that have already been backed, in a single click. COLLECT PHOTOS: Went to a party and want to collect all the photos in one place? Just share a link with your friends and ask them to upload. PARTNER SHARING: Share your camera album with your partner so they can automatically see your photos on their device. LEGACY: Allow trusted contacts to access your account in your absence. DARK & LIGHT THEMES: Choose the mode that will make your photos pop. ADDITIONAL SECURITY: Turn on two-factor authentication or set a lock-screen for the app. OPEN-SOURCE AND AUDITED: Ente Photos’s code is open-source, and has been audited by third-party security experts. HUMAN SUPPORT: We take pride in providing real human support. If you need help, reach out to [email protected], and one of us will be there to assist you. Keep your memories safe and private, with Ente Photos. Get started with 10 GB free. Terms: https://ente.io/terms
Rating
Version Info
- Current Versionv1.3.61
- Last Updated11 Aug 26
- First Released02 Dec 20
- Minimum iOS Version15.1
- Device Models Supported127
App Details
- IPA Size224.00 Mb
- PriceFree (USD)
- Age Advisory4+
- Supported Languages1
- DeveloperEnte Technologies, Inc.
- Bundle IDio.ente.frame
Screenshots

Ente Photos Socials
Discord
- Server Name
 Ente Community
- Member Count6961 (1064 online)
- Initial Channelinformation
- Invitervishnu
- Join Linkdiscord.com/invite/z2YVKkycX3
Ente Photos Reviews
More Photo Management
Self-hosted photo and video backup and management server, with automatic mobile upload, timeline view, albums, search and facial recognition. Needs to be self-hosted, but gives you full ownership + control over your photos.

About the Data: Ente Photos
Change History
- Added #626
Edit Ente Photos Data
You can edit Ente Photos's entry in this section of awesome-privacy.yml by submitting a PR to our GitHub repo.
Note that some of the information shown above has been aggregated from external
sources, a list of these can be found data documentation.
Origin Data
Modify Data
API
You can access Ente Photos's data programmatically via our API. Simply make a GET request to:
https://api.awesome-privacy.xyz/v1/services/ente-photosThe REST API is free, no-auth and CORS-enabled. To learn more, view the API Docs or read the API Usage Guide.
Share Ente Photos
Help your friends compare Photo Management, and pick privacy-respecting software and services.
Share Ente Photos and Awesome Privacy with your network!