Blokada
blokada.org
This application blocks ads and trackers, doesn't require root and works for all the apps on your Android phone. Check out how it works here.
- Homepage:blokada.org
- GitHub:github.com/blokadaorg/blokada
- Privacy:community.blokada.org/t/privacy-policy
- iOS App:apps.apple.com/us/app/blokada/id1508341781
- Android App:play.google.com/.../org.blokada.sex
- Web info:web-check.xyz/check/blokada.org
Blokada Source Code
Author
Description
The official repo for Blokada apps.
Homepage
https://blokada.orgRepository
- LicenseMPL-2.0
- Created19 Nov 16
- Primary languageDart
- Size157,546 KB
- Stars3,265
- Forks229
- Watchers3,265
Top Contributors
@kar (719)
@balboah (186)
@dependabot[bot] (115)
@blokada-ci[bot] (17)
@claude (3)
@Copilot (3)
Recent Commits
sync: update translate strings to: 0bbf (#1305) Co-authored-by: blokada-ci[bot] <276300274+blokada-ci[bot]@users.noreply.github.com>
ci: pass step outputs to job summaries via env (#1304) The Summary steps in the Dependabot auto-merge, release and promote workflows wrote step outputs into their scripts with ${{ }}. Read them from env instead, so free text such as the review reason prints verbatim. The auto-merge summary moves into its own job that needs no token permissions. Claude-Session: https://claude.ai/code/session_015GSdFdMhYUQEH9xnAgjBFW Co-authored-by: Claude <[email protected]>
sync: update translate strings to: af19e (#1303) Co-authored-by: blokada-ci[bot] <276300274+blokada-ci[bot]@users.noreply.github.com>
ci: state workflow token permissions explicitly (#1302) The last two workflows without a top-level permissions block relied on the repo's default token setting, which is being switched to read-only (issue-tracker#408). check-adapty-fallback only checks out; the Dependabot auto-merge jobs outside review act through the blokada-ci App token and need nothing from GITHUB_TOKEN. Co-authored-by: Claude Opus 5.5 <[email protected]>
fix(android): report tablet paywall dismissals to flutter (#1292) * fix(android): report tablet paywall dismissals to flutter The centered tablet paywall (AdaptyPaymentTabletDialogFragment) never reported its close when dismissed by the system back button or a rotation, because those paths skip PaymentBinding.closePaymentScreen and onFlowClosed is empty. PaymentActor._isOpened then stayed true and every later CTA tap returned early, so the paywall could not be reopened. - both paywall fragments now call PaymentBinding.handleFragmentDestroyed from onDestroy; it reports the close only for the current fragment and clears _fragment, so a dismissed fragment is no longer retained - clear _fragment before removing a stale fragment in doShowPaymentScreen so its onDestroy does not report a close for the open in progress - drop _currentView after it is handed to a fragment; it cannot be reused and otherwise kept the Activity it was built with alive Validation (Pixel Tablet API 34 emulator, 550dp letterboxed window, local hack keeping the paywall open since the image has no Play billing): - before: back dismisses, no PAYMENTHANDLESCREENCLOSED, CTA dead - after: back, Adapty close button and rotation each send exactly one close; paywall reopens after each - bottom sheet path (400dp): back then reopen still works - outside taps do not dismiss this dialog (activity theme) make test skipped: Flutter-only, change is Kotlin-only; the six debug APK build is the compile check. Co-Authored-By: Claude Opus 5.5 <[email protected]> * fix(android): drop the shown flow view when the paywall fragment is destroyed A back press or rotation dismisses the fragment without closePaymentScreen, so the view stayed referenced until the next open. Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude Opus 5.5 <[email protected]>
fix(android): close the paywall and show a failure modal on flow errors (#1290) * fix(android): close the paywall and show a failure modal on flow errors Adapty 4 reports flow rendering failures through onError, which only logged. The sheet stayed open with nothing drawn and Flutter was never told. Now onError closes a showing sheet and reports a temporary failure, as a products-loading failure already does, and drops the cached view so the next open fetches a fresh one. closePaymentScreen uses dismissAllowingStateLoss, since these callbacks can arrive after the activity saved its state. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_011UzDgDTbnuTVFQT5Ks4nwV * fix(android): only close the paywall for errors from the view on screen The flow listener was shared by every view, so an error from a preloaded or replaced view could close a working paywall. Each view now gets its own listener that delegates to PaymentBinding and passes the view to the error handler. Also log the Adapty error code and underlying cause. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_011UzDgDTbnuTVFQT5Ks4nwV * fix(android): keep the paywall open for recoverable flow errors Adapty UI also reports a broken image (shown as a placeholder), an invalid action URL and a missing navigator through onError. The flow keeps rendering in those cases, so only log them. Script errors and any other code still close the sheet. Co-Authored-By: Claude Opus 5.5 <[email protected]> Claude-Session: https://claude.ai/code/session_011UzDgDTbnuTVFQT5Ks4nwV * fix(android): only close the paywall on JS_EXCEPTION before the flow rendered Adapty UI 4.0.2 also reports individual script-call errors as JS_EXCEPTION, which can leave a working flow. Track onFlowShown per view in FlowListener: errors before it (flow script failed to load) still close the sheet and show the temporary-failure modal, errors after it are only logged. Unknown codes follow the same rule. Verified on a Galaxy S8 with a forced JS_EXCEPTION (reflection-built AdaptyError): before onFlowShown the sheet closed with the 'Payments are unavailable' modal; after it the paywall stayed open and usable. make test: 492 passed (unchanged, no Android unit tests). Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude <[email protected]>
fix(payment): read restore flag from the second checkout arg (#1291) - cmdCheckout read args[0] (profileId) for the restore flag, so restore was always false on the Android six path: a failed restore showed paymentFailed instead of accountRestoreFailed - a successful Android restore now also emits paymentSuccessful with restore=true, so it skips the Private DNS onboarding modal and the activity-logging reminder, matching iOS - register paymentHandleScreenClosed with argsNum: 1; Android sends one arg and argsNum: 0 skipped validation while args[0] was still read - add PaymentCommand arg-parsing tests; two of three fail on the old code Validation: make test (495 pass), fvm flutter analyze (no issues in changed files), /code-review high. Ref: blokadaorg/blokada#1290 (where the bug was spotted) Co-authored-by: Claude Opus 5.5 <[email protected]>
ci: build pull requests on hosted runners (#1300) PR code is untrusted -- a dependency bump runs third-party code -- and the three build jobs ran it on the long-lived self-hosted Mac (issue-tracker#408). They now run on GitHub-hosted runners, a fresh VM per job: Flutter analyze and the Android assemble on ubuntu-latest, the iOS build on the xcode-27 image the release archive uses. The Go setup for the WireGuard bridge moves into a shared action, used by both this workflow and ci-release. Nothing targets the build-only label any more; the Mac is left with the Appium jobs, which need its phone. Co-authored-by: Claude Opus 5.5 <[email protected]>
fix(six): keep modal sheet content above the Android navigation bar (#1301) The MainActivity is edge-to-edge, so modal sheets drawn by the shared BottomManagerSheet extended under the navigation bar and the Private DNS sheet's Open Settings button was partly covered. Add the bottom view padding to the shared Android sheet wrapper, which fixes every modal using it. Verified on an API 34 emulator with 3-button and gesture navigation. Tests: 492 passed before and after (no new tests; layout only). Co-authored-by: Claude Opus 5.5 <[email protected]>
fix(ci): pin fastlane for promote-android on the hosted runner (#1299) * fix(ci): pin fastlane for promote-android on the hosted runner promote-android writes an already-uploaded version code to a track by passing only --version_codes_to_retain. fastlane 2.237.0 closed that path (fastlane#30073), and moving promote to ubuntu-latest (#1298) swapped the Mac's global 2.228.0 for the image's 2.240.1. Both Android legs of run 37286722401 failed with 'Could not find release for version code' before anything was committed to Play. Pin the release the Mac promoted with. Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci: TEMP verify the pinned fastlane on ubuntu Drop before merge. Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci: drop the temporary pinned-fastlane verification workflow Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude Opus 5.5 <[email protected]>
ci(release): build and publish on hosted runners, behind a release environment (#1298) * ci(release): build and publish on hosted runners, behind a release environment Release and promote ran on the same long-lived self-hosted Mac as PR CI, so anything a PR left on that host would run again inside the next job holding the signing and store keys (issue-tracker#408). - Every ci-release and promote job now runs on a GitHub-hosted runner, a fresh VM per job. Android and the tag/allocate jobs move to ubuntu-latest, the iOS archive to the xcode-27 image (same Xcode 27.0 build as the Mac). - iOS signing comes from the match repo into a throwaway keychain (new ci_signing lane) instead of the host's login keychain. - Jobs that hold keys name the `release` environment, which only deploys from main. - fvm and Flutter are installed per job by a new setup-flutter action, with fvm pinned by digest. Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci: TEMP verify the hosted release toolchain on this PR Drop before merge. Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci: TEMP verify the hosted release toolchain on this PR Drop before merge. Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci(release): install Go 1.22 for the WireGuard bridge on the hosted iOS runner Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci: drop the temporary hosted-runner verification workflow Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude Opus 5.5 <[email protected]>
build(deps-dev): bump the appium-wdio-npm group (#1296) Bumps the appium-wdio-npm group in /automation/appium/wdio with 2 updates: [@types/node](https://github.com/DefinitelyTyped/DefinitelyTyped/tree/HEAD/types/node) and [chai](https://github.com/chaijs/chai). Updates `@types/node` from 26.6.2 to 26.6.4 - [Release notes](https://github.com/DefinitelyTyped/DefinitelyTyped/releases) - [Commits](https://github.com/DefinitelyTyped/DefinitelyTyped/commits/HEAD/types/node) Updates `chai` from 6.2.2 to 6.3.0 - [Release notes](https://github.com/chaijs/chai/releases) - [Changelog](https://github.com/chaijs/chai/blob/main/History.md) - [Commits](https://github.com/chaijs/chai/compare/v6.2.2...v6.3.0) --- updated-dependencies: - dependency-name: "@types/node" dependency-version: 26.6.4 dependency-type: direct:development update-type: version-update:semver-patch dependency-group: appium-wdio-npm - dependency-name: chai dependency-version: 6.3.0 dependency-type: direct:development update-type: version-update:semver-minor dependency-group: appium-wdio-npm ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump syncfusion_flutter_charts in /common (#1295) Bumps [syncfusion_flutter_charts](https://github.com/syncfusion/flutter-widgets/tree/master/packages) from 34.2.9 to 35.1.37. - [Release notes](https://github.com/syncfusion/flutter-widgets/releases) - [Commits](https://github.com/syncfusion/flutter-widgets/commits/HEAD/packages) --- updated-dependencies: - dependency-name: syncfusion_flutter_charts dependency-version: 35.1.37 dependency-type: direct:production update-type: version-update:semver-major ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump cupertino_icons from 1.0.9 to 2.0.0 in /common (#1294) Bumps [cupertino_icons](https://github.com/flutter/packages/tree/main/third_party/packages) from 1.0.9 to 2.0.0. - [Release notes](https://github.com/flutter/packages/releases) - [Commits](https://github.com/flutter/packages/commits/cupertino_icons-v2.0.0/third_party/packages) --- updated-dependencies: - dependency-name: cupertino_icons dependency-version: 2.0.0 dependency-type: direct:production update-type: version-update:semver-major ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump anthropics/claude-code-action (#1297) Bumps the github-actions group with 1 update: [anthropics/claude-code-action](https://github.com/anthropics/claude-code-action). Updates `anthropics/claude-code-action` from 1.0.235 to 1.0.240 - [Release notes](https://github.com/anthropics/claude-code-action/releases) - [Commits](https://github.com/anthropics/claude-code-action/compare/756cc22e19660d20e8cc9496b4f242475a7f7790...ed670b4cf9de2a5a570d130d2f6197b9e543cd64) --- updated-dependencies: - dependency-name: anthropics/claude-code-action dependency-version: 1.0.240 dependency-type: direct:production update-type: version-update:semver-patch dependency-group: github-actions ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump the flutter-dependencies group (#1293) Bumps the flutter-dependencies group in /common with 4 updates: [build_runner](https://github.com/dart-lang/build), [cached_network_image](https://github.com/Baseflow/flutter_cached_network_image), [mobx_codegen](https://github.com/mobxjs/mobx.dart) and [mockito](https://github.com/dart-lang/build/tree/master/builder_pkgs). Updates `build_runner` from 2.4.13 to 2.15.1 - [Release notes](https://github.com/dart-lang/build/releases) - [Commits](https://github.com/dart-lang/build/compare/build_runner-v2.4.13...build_runner-v2.15.1) Updates `cached_network_image` from 4.0.2 to 4.0.3 - [Release notes](https://github.com/Baseflow/flutter_cached_network_image/releases) - [Commits](https://github.com/Baseflow/flutter_cached_network_image/compare/v4.0.2...v4.0.3) Updates `mobx_codegen` from 2.6.2 to 2.7.8 - [Release notes](https://github.com/mobxjs/mobx.dart/releases) - [Changelog](https://github.com/mobxjs/mobx.dart/blob/main/CHANGELOG.md) - [Commits](https://github.com/mobxjs/mobx.dart/compare/mobx_codegen-2.6.2...mobx_codegen-2.7.8) Updates `mockito` from 5.4.4 to 5.6.4 - [Release notes](https://github.com/dart-lang/build/releases) - [Commits](https://github.com/dart-lang/build/commits/mockito-v5.6.4/builder_pkgs) --- updated-dependencies: - dependency-name: build_runner dependency-version: 2.15.1 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: flutter-dependencies - dependency-name: cached_network_image dependency-version: 4.0.3 dependency-type: direct:production update-type: version-update:semver-patch dependency-group: flutter-dependencies - dependency-name: mobx_codegen dependency-version: 2.7.8 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: flutter-dependencies - dependency-name: mockito dependency-version: 5.6.4 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: flutter-dependencies ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump the appium-wdio-npm-security group across 1 directory with 2 updates (#1289) Bumps the appium-wdio-npm-security group with 2 updates in the /automation/appium/wdio directory: [brace-expansion](https://github.com/juliangruber/brace-expansion) and [serialize-javascript](https://github.com/yahoo/serialize-javascript). Updates `brace-expansion` from 2.1.4 to 2.1.7 - [Release notes](https://github.com/juliangruber/brace-expansion/releases) - [Commits](https://github.com/juliangruber/brace-expansion/compare/v2.1.4...v2.1.7) Updates `serialize-javascript` from 7.1.1 to 7.1.2 - [Release notes](https://github.com/yahoo/serialize-javascript/releases) - [Commits](https://github.com/yahoo/serialize-javascript/compare/v7.1.1...v7.1.2) --- updated-dependencies: - dependency-name: brace-expansion dependency-version: 2.1.7 dependency-type: indirect dependency-group: appium-wdio-npm-security - dependency-name: serialize-javascript dependency-version: 7.1.2 dependency-type: indirect dependency-group: appium-wdio-npm-security ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
ci(release): strip TestFlight upload diagnostics, keep the early-failure retry (#1288) * ci(release): retry a failed TestFlight upload with altool directly, verbose The #1287 probe showed the runner reaches Apple's endpoint in 0.5s right before and after each failure, and --verbose passed through fastlane added nothing: the failing output is still two lines, without the banner and timestamped log lines the same altool 27.0.5 prints when run by hand. Run the retry as a direct altool --upload-app --verbose call so a failure shows altool's own log (first and last 150 lines, JWTs and URL query strings stripped, key and issuer ids masked). Also record the altool path, any installed iTMSTransporter, and proxy/fastlane-related env var names, and drop the unverified claim about when Defaults.properties is fetched. Co-Authored-By: Claude Opus 5.5 <[email protected]> * ci(release): strip TestFlight upload diagnostics, keep the early-failure retry Remove the debug-only parts added in #1287 and earlier on this branch: the pre-upload probe, the DNS/proxy dump, the fastlane --verbose passthrough and its output filter, and the direct altool --verbose retry that handled the App Store key in the workflow. Keep one retry through the normal make target when the upload fails within 180s, and a single curl timing probe that runs only on that failure path, so a successful run costs nothing extra. Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude Opus 5.5 <[email protected]>
ci(release): probe the network and retry a TestFlight upload that fails early (#1287) altool fetches contentdelivery.itunes.apple.com/transporter/Defaults.properties before uploading and exits with "The file Defaults.properties couldn't be opened" when that request times out after 60s. This has failed most release uploads on the runner since 2026-09-28, while the same URL answers in 0.5s from a shell on the same host. Capture evidence inside the failing job: run altool with --verbose, probe the endpoint over IPv4 and IPv6 plus DNS and proxy settings before the upload and after a failure, and retry once when the failure comes within 180s, before any bytes are sent. Co-authored-by: Claude Opus 5.5 <[email protected]>
chore(support): remove the purchase timeout support event (#1285) Family sent PURCHASE_TIMEOUT to the support chat backend 27s after the user left the paywall without buying, creating a chat session and a "new support message" notification. Remove the actor, its persisted flag, the supportNotify debug command (which only sent this event), the SupportEvent value, and the now-unused SupportActor.onReset and PaymentActor.onPaymentScreenOpened hooks. Claude-Session: https://claude.ai/code/session_016gzddxqsuZx9C4pNVWiZXc Co-authored-by: Claude <[email protected]>
fix(ios): exempt captive-portal login domains from the DoH profile (#1275) * fix(ios): exempt captive-portal probes from the DoH profile The Cloud/Family DoH profile also caught iOS's captive-portal probe (captive.apple.com), so walled-garden wifi never showed the sign-in sheet and looked like no internet. Add NEDNSSettingsManager.onDemandRules that send Apple's probe hosts to system DNS, with a trailing Connect rule so DoH keeps filtering everything else. Existing users pick this up on the next launch, since the profile is re-saved on every start. Refs blokadaorg/issue-tracker#283 Co-Authored-By: Claude Opus 5.5 (1M context) <[email protected]> * fix(ios): exempt captive-portal login domains from the DoH profile Testing showed iOS already exempts its own captive probe from DNS profiles; what breaks is the portal's login page opened in Safari, whose host often exists only in the portal network's DNS (e.g. wifi.finnair.com is NXDOMAIN publicly). Extend the neverConnect list with known in-flight, rail and hotel-platform portal hosts, keeping Apple's probe hosts as a hedge for networks where no sheet appears. Refs blokadaorg/issue-tracker#283 Co-Authored-By: Claude Opus 5.5 (1M context) <[email protected]> Claude-Session: https://claude.ai/code/session_01PHms5UiGbdr44cLAS922fK * fix(ios): drop the GlobalReach corporate domain from the portal list globalreachtech.com is the vendor's corporate site, not a portal host. Their portals are served from the Odyssys platform domain, which stays. Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude Opus 5.5 (1M context) <[email protected]>
sync: update translate strings to: b52bd (#1286) Co-authored-by: blokada-ci[bot] <276300274+blokada-ci[bot]@users.noreply.github.com>
sync: update translate strings to: 9c237 (#1284) Co-authored-by: blokada-ci[bot] <276300274+blokada-ci[bot]@users.noreply.github.com>
fix(payment): explain a restore that finds no active purchase (#1283) * fix(payment): explain a restore that finds no active purchase (#395) Since the #376 guard, a restore with no active access level returned silently, so the Restore button looked broken. Show an Adapty dialog over the paywall (our own modals render beneath it) and keep the paywall open so the user can still buy. One message covers both never-bought and expired: the Adapty profile's access levels belong to the Blokada account, not the store account being restored, so they can't tell those apart. Co-Authored-By: Claude Opus 5.5 <[email protected]> * sync: update translate strings to: f707 Co-Authored-By: Claude Opus 5.5 <[email protected]> * fix(payment): use the reworded restore-not-found string Co-Authored-By: Claude Opus 5.5 <[email protected]> * sync: update translate strings to: 1b60 Co-Authored-By: Claude Opus 5.5 <[email protected]> * sync: update translate strings to: 5cc3f Co-Authored-By: Claude Opus 5.5 <[email protected]> --------- Co-authored-by: Claude Opus 5.5 <[email protected]>
sync: update translate strings to: 7c2e (#1282) Co-authored-by: blokada-ci[bot] <276300274+blokada-ci[bot]@users.noreply.github.com>
build(deps): bump ip-address (#1281) Bumps the appium-wdio-npm-security group with 1 update in the /automation/appium/wdio directory: [ip-address](https://github.com/beaugunderson/ip-address). Updates `ip-address` from 10.4.0 to 10.7.2 - [Release notes](https://github.com/beaugunderson/ip-address/releases) - [Commits](https://github.com/beaugunderson/ip-address/compare/v10.4.0...v10.7.2) --- updated-dependencies: - dependency-name: ip-address dependency-version: 10.7.2 dependency-type: indirect dependency-group: appium-wdio-npm-security ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump the android-gradle group in /android with 5 updates (#1278) Bumps the android-gradle group in /android with 5 updates: | Package | From | To | | --- | --- | --- | | androidx.navigation:navigation-safe-args-gradle-plugin | `2.10.1` | `2.10.2` | | androidx.core:core-ktx | `1.19.0` | `1.19.1` | | androidx.annotation:annotation | `1.10.0` | `1.11.0` | | androidx.fragment:fragment-ktx | `1.9.0` | `1.9.1` | | [gradle-wrapper](https://github.com/gradle/gradle) | `9.7.1` | `9.8.0` | Updates `androidx.navigation:navigation-safe-args-gradle-plugin` from 2.10.1 to 2.10.2 Updates `androidx.core:core-ktx` from 1.19.0 to 1.19.1 Updates `androidx.annotation:annotation` from 1.10.0 to 1.11.0 Updates `androidx.fragment:fragment-ktx` from 1.9.0 to 1.9.1 Updates `gradle-wrapper` from 9.7.1 to 9.8.0 - [Release notes](https://github.com/gradle/gradle/releases) - [Commits](https://github.com/gradle/gradle/compare/v9.7.1...v9.8.0) --- updated-dependencies: - dependency-name: androidx.navigation:navigation-safe-args-gradle-plugin dependency-version: 2.10.2 dependency-type: direct:production update-type: version-update:semver-patch dependency-group: android-gradle - dependency-name: androidx.core:core-ktx dependency-version: 1.19.1 dependency-type: direct:production update-type: version-update:semver-patch dependency-group: android-gradle - dependency-name: androidx.annotation:annotation dependency-version: 1.11.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: android-gradle - dependency-name: androidx.fragment:fragment-ktx dependency-version: 1.9.1 dependency-type: direct:production update-type: version-update:semver-patch dependency-group: android-gradle - dependency-name: gradle-wrapper dependency-version: 9.8.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: android-gradle ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump rubyzip from 2.4.1 to 3.4.0 in /ios (#1276) Bumps [rubyzip](https://github.com/rubyzip/rubyzip) from 2.4.1 to 3.4.0. - [Release notes](https://github.com/rubyzip/rubyzip/releases) - [Changelog](https://github.com/rubyzip/rubyzip/blob/main/Changelog.md) - [Commits](https://github.com/rubyzip/rubyzip/compare/v2.4.1...v3.4.0) --- updated-dependencies: - dependency-name: rubyzip dependency-version: 3.4.0 dependency-type: indirect ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump anthropics/claude-code-action (#1280) Bumps the github-actions group with 1 update: [anthropics/claude-code-action](https://github.com/anthropics/claude-code-action). Updates `anthropics/claude-code-action` from 1.0.231 to 1.0.235 - [Release notes](https://github.com/anthropics/claude-code-action/releases) - [Commits](https://github.com/anthropics/claude-code-action/compare/cfc3eb22bfed5c26ef66e3223c982af27e4524de...756cc22e19660d20e8cc9496b4f242475a7f7790) --- updated-dependencies: - dependency-name: anthropics/claude-code-action dependency-version: 1.0.235 dependency-type: direct:production update-type: version-update:semver-patch dependency-group: github-actions ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
build(deps): bump the appium-wdio-npm group (#1279) Bumps the appium-wdio-npm group in /automation/appium/wdio with 7 updates: | Package | From | To | | --- | --- | --- | | [@wdio/cli](https://github.com/webdriverio/webdriverio/tree/HEAD/packages/wdio-cli) | `9.31.9` | `9.32.0` | | [@wdio/local-runner](https://github.com/webdriverio/webdriverio/tree/HEAD/packages/wdio-local-runner) | `9.31.9` | `9.32.0` | | [@wdio/mocha-framework](https://github.com/webdriverio/webdriverio/tree/HEAD/packages/wdio-mocha-framework) | `9.31.9` | `9.32.0` | | [@wdio/spec-reporter](https://github.com/webdriverio/webdriverio/tree/HEAD/packages/wdio-spec-reporter) | `9.31.2` | `9.32.0` | | [webdriverio](https://github.com/webdriverio/webdriverio/tree/HEAD/packages/webdriverio) | `9.31.9` | `9.32.0` | | [@wdio/junit-reporter](https://github.com/webdriverio/webdriverio/tree/HEAD/packages/wdio-junit-reporter) | `9.31.2` | `9.32.0` | | [appium](https://github.com/appium/appium/tree/HEAD/packages/appium) | `3.7.0` | `3.8.0` | Updates `@wdio/cli` from 9.31.9 to 9.32.0 - [Release notes](https://github.com/webdriverio/webdriverio/releases) - [Changelog](https://github.com/webdriverio/webdriverio/blob/main/CHANGELOG.md) - [Commits](https://github.com/webdriverio/webdriverio/commits/v9.32.0/packages/wdio-cli) Updates `@wdio/local-runner` from 9.31.9 to 9.32.0 - [Release notes](https://github.com/webdriverio/webdriverio/releases) - [Changelog](https://github.com/webdriverio/webdriverio/blob/main/CHANGELOG.md) - [Commits](https://github.com/webdriverio/webdriverio/commits/v9.32.0/packages/wdio-local-runner) Updates `@wdio/mocha-framework` from 9.31.9 to 9.32.0 - [Release notes](https://github.com/webdriverio/webdriverio/releases) - [Changelog](https://github.com/webdriverio/webdriverio/blob/main/CHANGELOG.md) - [Commits](https://github.com/webdriverio/webdriverio/commits/v9.32.0/packages/wdio-mocha-framework) Updates `@wdio/spec-reporter` from 9.31.2 to 9.32.0 - [Release notes](https://github.com/webdriverio/webdriverio/releases) - [Changelog](https://github.com/webdriverio/webdriverio/blob/main/CHANGELOG.md) - [Commits](https://github.com/webdriverio/webdriverio/commits/v9.32.0/packages/wdio-spec-reporter) Updates `webdriverio` from 9.31.9 to 9.32.0 - [Release notes](https://github.com/webdriverio/webdriverio/releases) - [Changelog](https://github.com/webdriverio/webdriverio/blob/main/CHANGELOG.md) - [Commits](https://github.com/webdriverio/webdriverio/commits/v9.32.0/packages/webdriverio) Updates `@wdio/junit-reporter` from 9.31.2 to 9.32.0 - [Release notes](https://github.com/webdriverio/webdriverio/releases) - [Changelog](https://github.com/webdriverio/webdriverio/blob/main/CHANGELOG.md) - [Commits](https://github.com/webdriverio/webdriverio/commits/v9.32.0/packages/wdio-junit-reporter) Updates `appium` from 3.7.0 to 3.8.0 - [Release notes](https://github.com/appium/appium/releases) - [Changelog](https://github.com/appium/appium/blob/master/packages/appium/CHANGELOG.md) - [Commits](https://github.com/appium/appium/commits/[email protected]/packages/appium) --- updated-dependencies: - dependency-name: "@wdio/cli" dependency-version: 9.32.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: appium-wdio-npm - dependency-name: "@wdio/local-runner" dependency-version: 9.32.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: appium-wdio-npm - dependency-name: "@wdio/mocha-framework" dependency-version: 9.32.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: appium-wdio-npm - dependency-name: "@wdio/spec-reporter" dependency-version: 9.32.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: appium-wdio-npm - dependency-name: webdriverio dependency-version: 9.32.0 dependency-type: direct:production update-type: version-update:semver-minor dependency-group: appium-wdio-npm - dependency-name: "@wdio/junit-reporter" dependency-version: 9.32.0 dependency-type: direct:development update-type: version-update:semver-minor dependency-group: appium-wdio-npm - dependency-name: appium dependency-version: 3.8.0 dependency-type: direct:development update-type: version-update:semver-minor dependency-group: appium-wdio-npm ... Signed-off-by: dependabot[bot] <[email protected]> Co-authored-by: dependabot[bot] <49699333+dependabot[bot]@users.noreply.github.com>
Blokada Security
Blokada Website
Website
Blokada - the popular mobile adblocker and VPN for Android and iOS
Keep all your devices protected with Blokada content filtering and encryption.
Redirects
Does not redirect
Security Checks
All 65 security checks passed
Server Details
- IP Address104.21.26.94
- LocationSan Francisco,California,United States of America,NA
- ISPCloudFlare Inc.
- ASNAS13335
Associated Countries
 US
 CA
Safety Score
Website marked as safe
100%
Trackers
No known trackers found
Blacklist Check
blokada.org was found on 0 blacklists
- AntiSocial Blacklist
- Artists Against 419
- Badbitcoin
- Bambenek Consulting
- CERT Polska
- CoinBlockerLists
- CRDF
- CryptoScamDB
- EtherAddressLookup
- EtherScamDB
- Fake Website Buster
- MetaMask EthPhishing
- NABP Not Recommended Sites
- OpenPhish
- PetScams
- PhishFeed
- PhishFort
- Phishing.Database
- PhishStats
- PhishTank
- Phishunt
- RPiList Not Serious
- Scam.Directory
- SecureReload Phishing List
- Spam404
- StopGunScams
- Suspicious Hosting IP
- ThreatFox
- ThreatLog
- TweetFeed
- URLhaus
- ViriBack C2 Tracker
Website Preview

Blokada Android App
APK Info
- AppBlokada 6
- Creation Date28 May 24
- Last Updated14 Jul 24
- Current Version24.1.2
- Privacy ReportView on Exodus →
Trackers
No trackers found
Permissions
- Access Coarse Location
- Access Network State
- Access Wifi State
- Foreground Service
- Get Tasks
- Interact Across Users
- Internet
- Post Notifications
- Read Logs
- Read Phone State
- Receive Boot Completed
- Request Delete Packages
- Use Biometric
- Use Fingerprint
- Vibrate
- Wake Lock
- Write External Storage
- Set Alarm
- Billing
- Dynamic Receiver Not Exported Permission
Blokada iOS App
App Info
 Ad Blocker VPN & DNS – Blokada
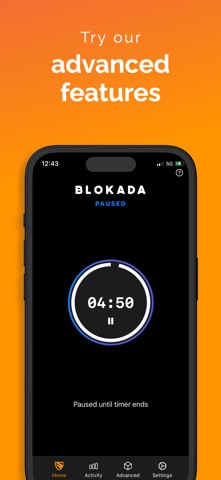
This is the official app on App Store from the Blokada open source project. Blokada for iOS uses DNS (Domain Name System) to enable you to have an ad free experience to see only the content you want. Use Blokada Cloud to block ads and trackers, while keeping your DNS traffic confidential. Upgrade to Blokada Plus for encrypting all traffic with our global VPN network. Improve your privacy and secure your Internet against cyber attacks and hackers. ---- Top features: - Supports ad-blocking for every web browser and other app installed. - Blocks sites that distribute malicious content, viruses and fraudulent websites. - DNS based interception for all modern browsers and apps. - Fast and reliable VPN that protects your privacy and encrypts your data. The most compatible ad blocker on the market! • Blocks ads • Saves your data plan • Browse FASTER by loading less data • Increase your battery life What can be blocked? • Block annoying ads: Google AdWords, Google Invite Media, DoubleClick Bid Manager, Liftoff, Bing Ads, Amazon, etc • Block adult websites • Block gambling websites • Block social media trackers: Google Analytics, Facebook Connect, DoubleClick, Google Publisher Tags, Google AdSense, Twitter Button, Yandex.Metrix, Comscore • Block malicious websites: Virus downloads, malicious content, fraudulent websites and manipulated apps ---- Terms of Use: https://go.blokada.org/terms Privacy Policy: https://go.blokada.org/privacy
Rating
Version Info
- Current Version26.8.1020
- Last Updated28 Aug 26
- First Released06 Jun 20
- Minimum iOS Version15.0
- Device Models Supported127
App Details
- IPA Size68.97 Mb
- PriceFree (USD)
- Age Advisory4+
- Supported Languages17
- DeveloperBlocka AB
- Bundle IDnet.blocka.app
Screenshots




Blokada Reviews
More Mobile Apps
Lets you use CloudFlares fast and secure 1.1.1.1 DNS, with DNS over HTTPS, and also has the option to enable CloudFlares WARP+ VPN.
Android Firewall+ (AFWall+) is an advanced iptables editor (GUI) for rooted Android devices, which provides very fine-grained control over which Android apps are allowed to access the network. Get from F-Droid
Gives you the ability to grant permissions temporarily, so that you could for example use the camera to take a profile picture, but when you close the given app, those permissions will be revoked.
Prevent background processes gaining unauthorized access to your devices camera. Better still, use a webcam sticker.
Not Open SourceSimple tool, that compares SHA-1 fingerprints of the the SSL certificates seen from your device, and the certificate seen from an external network. If they do not match, this may indicate a man-in-the-middle modifying requests.
Encrypts files and folders client-side, before uploading them to cloud storage (such as Google Drive, One Drive or Dropbox), meaning none of your personal documents leave your device in plain text.
Shows which trackers, each of your installed apps is using, so that you can better understand how your data is being collected. Uses data from the Exodus database of scanned APKs.
F-Droid is an installable catalogue of FOSS applications for Android. The client enables you to browse, install, and keep track of updates on your device.
A network scanner to help you monitor and secure your WiFi network. The app is totally free, but to use the advanced controls, you will need a Fing Box.
Auto-disable Bluetooth, then it is not being used. Saves battery, and prevent some security risks. Get from F-Droid
An actively-maintained fork of the Island project with additional enhancements
A sandbox environment, allowing you to clone selected apps and run them in an isolated box, preventing it from accessing your personal data, or device information.
A firewall app for Android, which does not require root. NetGuard provides simple and advanced ways to block access to the internet, where applications and addresses can individually be allowed or denied access to your Wi-Fi and/or mobile connection.
System-wide Tor proxy, which encrypts your connection through multiple nodes. You can also use it alongside Tor Browser to access .onion sites.
An open-source ad-blocker and firewall app for Android 6+ (does not require root).
Prevent background processes taking unauthorized screenshots, which could expose sensitive data.
Not Open SourceTriggers actions, when certain security conditions are met, such as multiple failed login attempts or monitor settings changed. It does require Tasker, and needs to be set up with ADB, device does not need to be rooted.
A radio frequency scanner app for Android with recon and offensive capabilities.
Makes it possible to entirely freeze all background activities on a per-app basis. Intended purpose is to speed up your phone, and prolong battery life, but this app is also a great utility to stop certain apps from collecting data and tracking your actions while running in the background. See on F-Droid
Monitor and control hidden data collection in mobile apps about user behavior/ tracking. Get from F-Droid







About the Data: Blokada
Change History
- Amended (androidApp, iosApp)
Edit Blokada Data
You can edit Blokada's entry in this section of awesome-privacy.yml by submitting a PR to our GitHub repo.
Note that some of the information shown above has been aggregated from external
sources, a list of these can be found data documentation.
Origin Data
Modify Data
API
You can access Blokada's data programmatically via our API. Simply make a GET request to:
https://api.awesome-privacy.xyz/v1/services/blokadaThe REST API is free, no-auth and CORS-enabled. To learn more, view the API Docs or read the API Usage Guide.
Share Blokada
Help your friends compare Mobile Apps, and pick privacy-respecting software and services.
Share Blokada and Awesome Privacy with your network!